Summarize this article with AI:
 Ask ChatGPT
 Ask Grok
 Ask Perplexity
 Ask Claude
 Ask Google AI
The Story: The Compliant Heist
PLUMP SPIDER Threat Overview: Brazil-Focused Financial Attacks
PLUMP SPIDER is a financially motivated threat actor known for targeting Brazil’s financial sector. Active since at least September 2023, the group has primarily targeted Brazilian banks, fintechs, payment service providers, and organizations connected to financial infrastructure.
Its use of native Brazilian Portuguese speakers and familiarity with local banking and support practices enable highly targeted social engineering against employees and other personnel with access to IT, identity, remote-support, or payment systems.
Its primary objective is financial fraud rather than ransomware. Credential and sensitive-data theft may be used as enabling steps, but the ultimate goal is to turn trusted access into payment authority.
PLUMP SPIDER Technical Attack Chain: From Initial Access to Pix Gateway Abuse
The attack chain typically begins with IT-support impersonation, using voice calls or messaging to pose as legitimate support personnel. Victims may be persuaded to install remote-management tools or execute attacker-supplied code, giving PLUMP SPIDER an initial foothold.
From there, the group works to move deeper into the environment while blending with trusted traffic. It uses legitimate remote-management software and encrypted VPN tunnels to make malicious communications resemble normal internal VPN activity. At the same time, communications with compromised .gov.br infrastructure can make external traffic appear to be reaching a trusted government entity. Together, these techniques can help evade firewall controls that rely on both traffic characteristics and destination reputation to identify suspicious activity.
Once inside, PLUMP SPIDER conducts network discovery and privilege escalation to expand access. A disguised PowerShell reconnaissance script associated with the activity maps the victim’s host, network, identity, and domain environment, then packages and transmits the collected data to attacker-controlled C2 infrastructure. This reconnaissance helps expose privileged accounts, credentials, certificates, API keys, and other authentication material that can provide access to core financial applications and payment systems.
The ultimate target is the bank’s Pix Gateway — the system used to send payments into Pix, Brazil’s instant-payment network. Once compromised, the gateway can be abused to create fraudulent pacs.008 payment instructions that appear to originate from the bank.
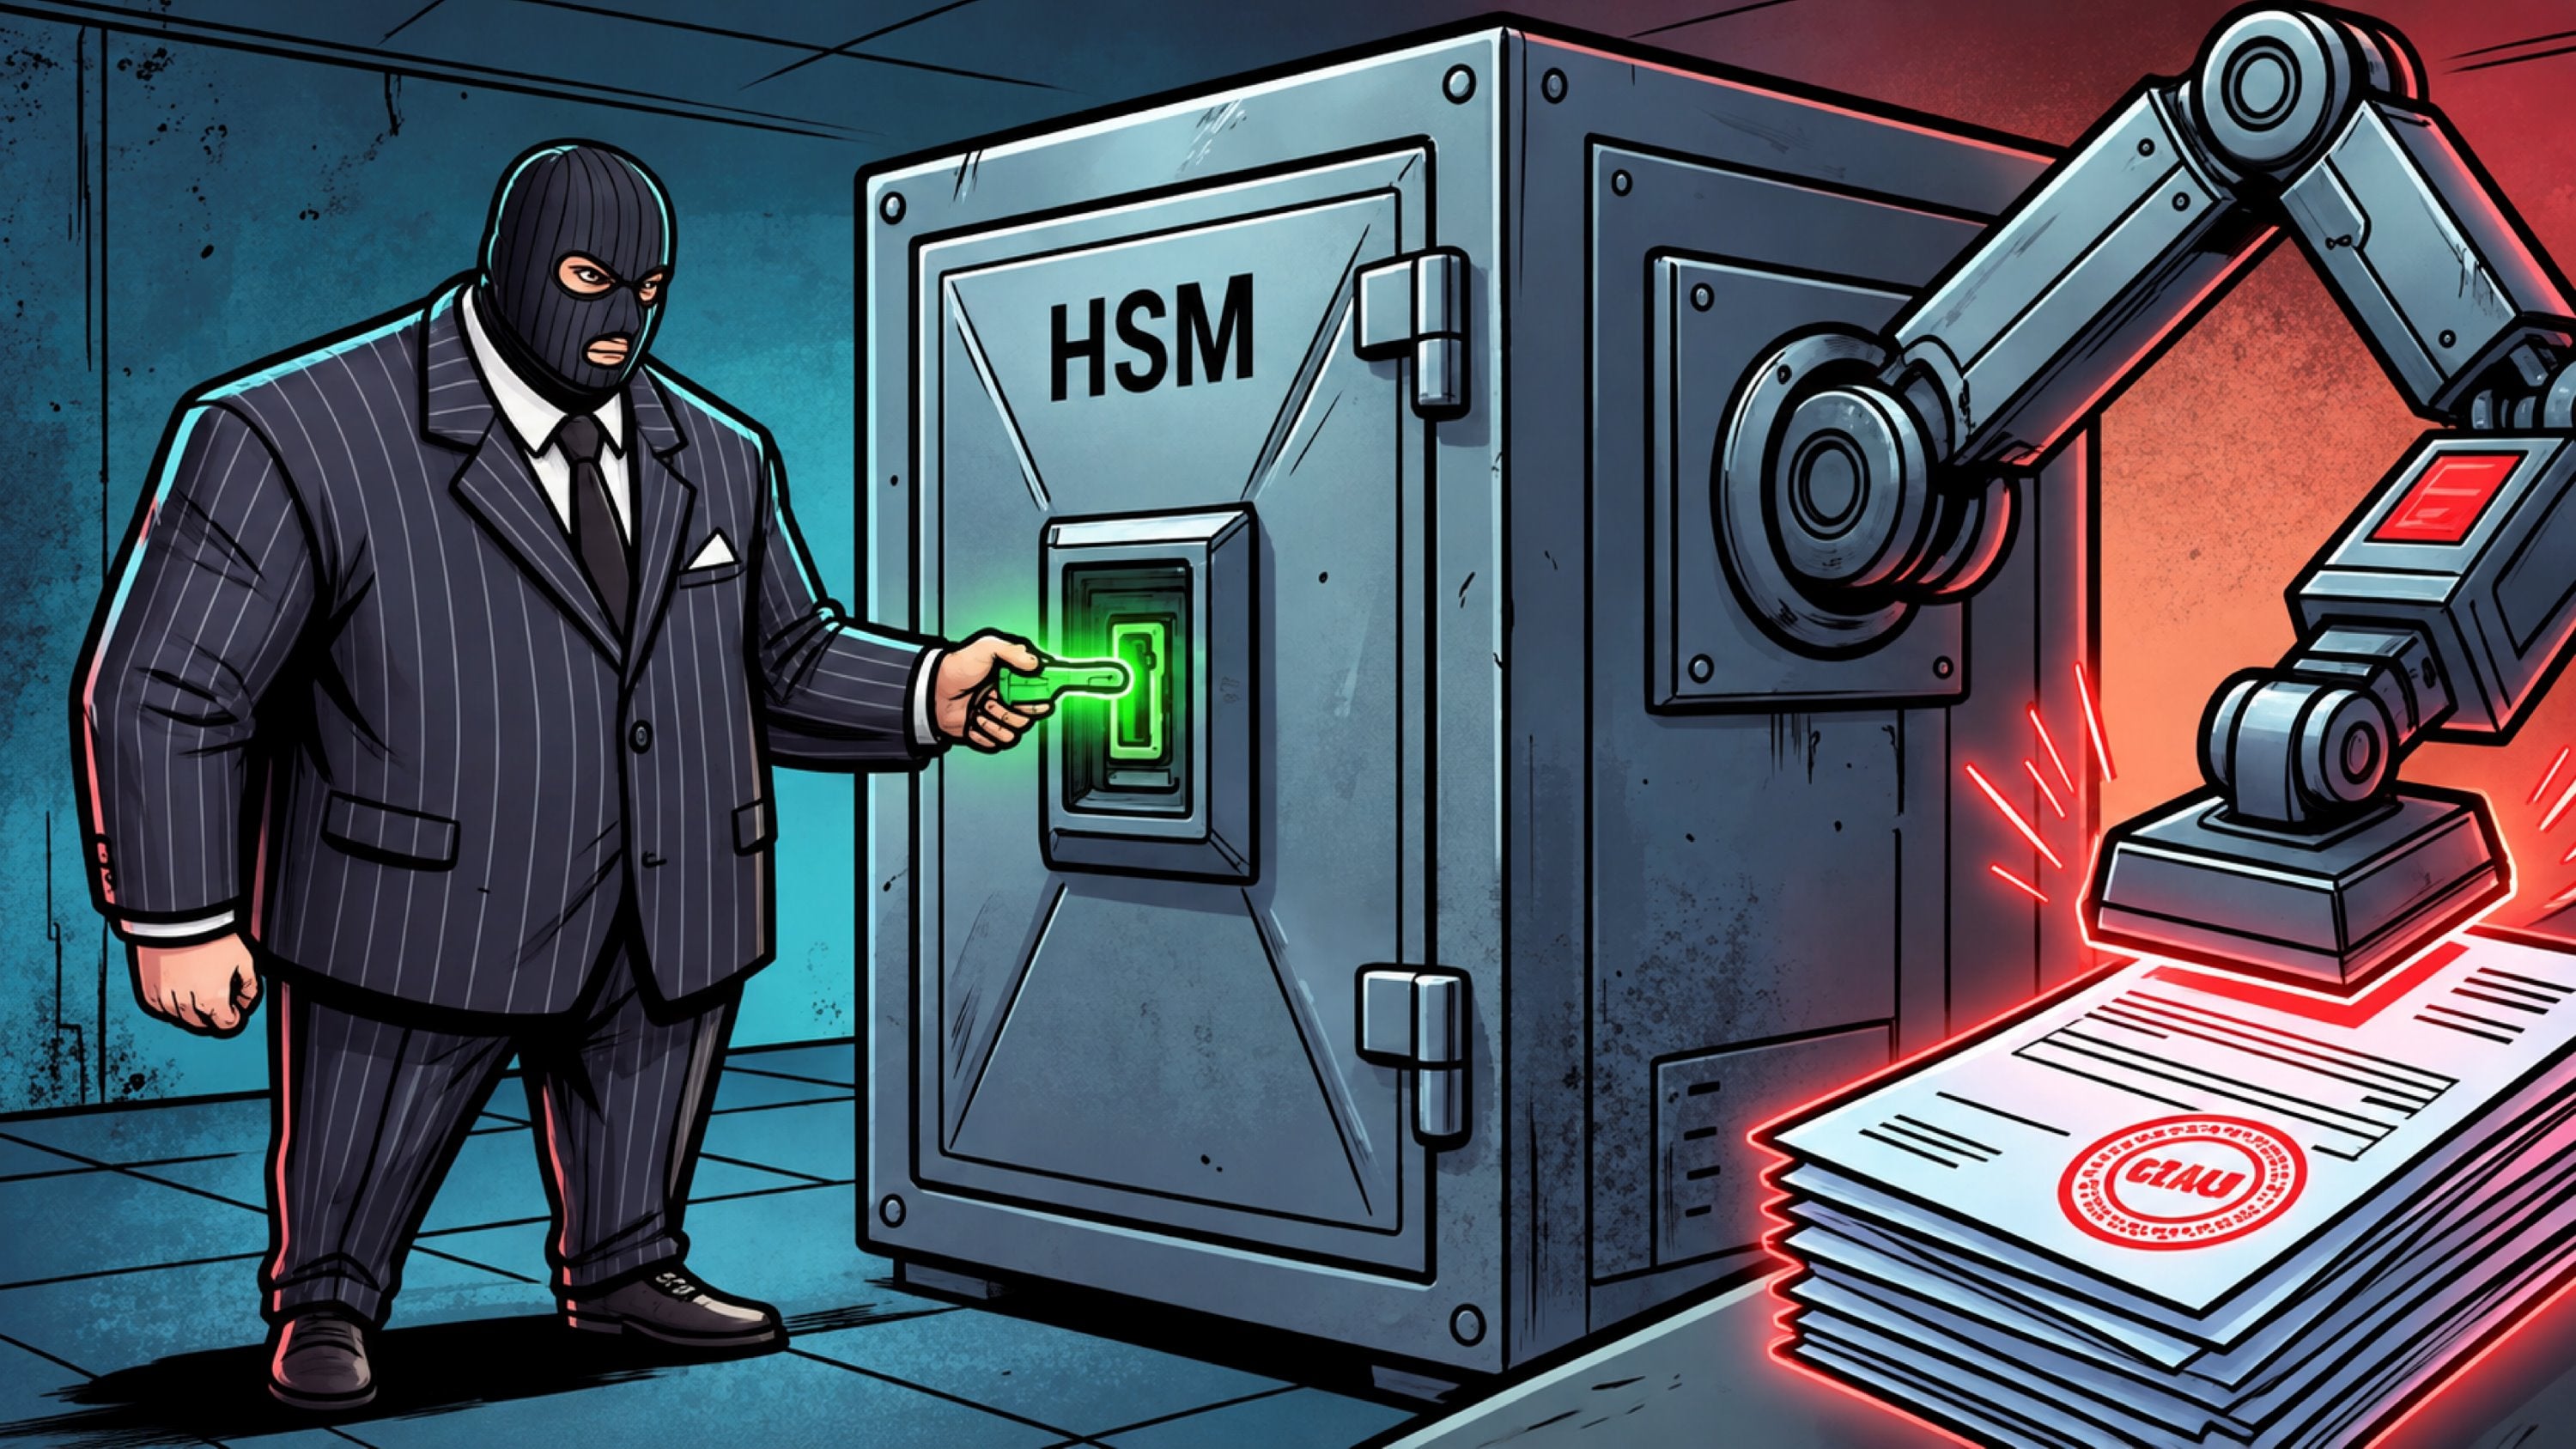
These payment instructions require a digital signature generated with the bank’s private signing key, which is protected inside a Hardware Security Module (HSM). Because the Pix Gateway is authorized to request those signatures, attackers controlling the gateway can feed fraudulent instructions into the legitimate signing process and obtain genuine bank signatures on fraudulent payments.
No signing key needs to be stolen and no cryptography needs to be broken. The attacker instead abuses the trusted relationship between the Pix Gateway and the HSM, turning fraudulent instructions into technically valid, bank-signed payments that can be submitted through Pix for real-time settlement.
Sangfor FarSight Labs Investigation: The aut-bank[.]com Surface
The public tradecraft above provides context for the actor. The FarSight Labs analysis below documents infrastructure and samples observed in this investigation; directly observed relationships are stated as findings, while actor-level links should be read alongside the external reporting in the Source Index.
Sample Communications Place the Domain in the Payload Chain
aut-bank[.]com (registered Sep 29, 2025) is assessed as malicious in this investigation, functioning as payload-delivery and C2-related infrastructure. ok.bat uses certutil to download JavaUpdate.jar and creates a SYSTEM startup task, while the JAR process handles victim registration/heartbeat and data exfiltration via multipart POST. Associated with multiple IPs (151.243.219[.]89, 24.152.36[.]138, 15.197.148[.]33, 3.33.130[.]190), the domain shows infrastructure migration and churn over time.
Defenders should correlate the domain, IPs, processes, and artifacts on a unified timeline to track infrastructure changes.
Brazilian Targeting Is Visible in the Infrastructure
The related names are not a random collection. solucaosuporte, painel-representantes, serprobr, plataforma10x, and enem10x draw on Portuguese-language support, representative-portal, service-platform, and Brazilian public-service or education themes. Other domains use randomized names such as raynfff, anryr, and kkujkqe. Combined with hosting nodes in São Paulo and Belo Horizonte, the naming and deployment pattern reflects preparation for Brazilian users and institutional environments.
Two Operational Infrastructure Sets
The first set centers on aut-bank[.]com and 151.243.219[.]89 and connects jyyyr[.]com, painel-representantes[.]com, serprobr[.]com, resumo.painelvinyjunior[.]com, and t2.painelvinyjunior[.]com. Portuguese-language support, representative-portal, and public-service themes give this cluster a clear Brazilian social-engineering and lure context. Together with confirmed payload download and data return, the relationships place aut-bank[.]com inside the same malicious delivery and social-engineering infrastructure cluster. Preserved evidence does not include a bank-login HTML page or screenshot on this domain, nor username, password, or OTP submissions, so a specific fake-bank portal on aut-bank[.]com is not claimed as fact.
The second set centers on 24.152.36[.]138 and connects plataforma10x[.]com[.]br, enem10x[.]com[.]br, raynfff[.]com, anryr[.]com, and kkujkqe[.]com with clouds.zip archives, Python-packaged executables, and a SoftEther-related archive. Related samples query their public egress address and then reach nuvem[.]host or rickcooder[.]nuvem[.]host, producing a useful environment-check-to-follow-on-connection sequence.
Key Relationship Chains
| Object | Observed relationship | Threat significance |
| aut-bank[.]com | Hosts JavaUpdate.jar and receives hostname/timestamp requests and multipart POSTs. | Payload delivery, host registration or heartbeat, reconnaissance return, and C2-related activity. |
| 151.243.219[.]89 | Historical resolution for aut-bank[.]com and a hub for Portuguese support, representative, and public-service themes. | Links confirmed malicious communications to a Brazil-oriented social-engineering and lure cluster. |
| 24.152.36[.]138 | Connects the second randomized-domain set with archives and executables. | Associated with payload delivery, remote channels, and follow-on C2 activity. |
| qvmsrb.exe | SHA-256: be0ebf760d550af033fe5a1da3c081262bd2e78f9b1f0e5778ccbf030a553dc3 | Supports multi-version tracking of one build family. Shared characteristics: TLSH, SSDEEP, and IMPHASH similarities; Python-packaged runtime artifacts. |
| a0b6ioc2.exe | SHA-256: d2e5d7669524473686efd5efbdcdd84463b7328ace122951fc76ab4c52cd2298 |
What the IOC Details Reveal About the Multi-Stage Payload Chain
ok.bat → JavaUpdate.jar → Registration and Data Return
The entry file ok.bat has SHA-256
f8339e5fbaee413b8154d83e313e4e4edb499c9c09de618353e20e7685166924.
At approximately 3 KB, it carries long-sleep and debugger-environment detection tags. Recorded commands show it using certutil to download http[:]//aut-bank[.]com/JavaUpdate.jar and creating a SYSTEM startup scheduled task for persistence. The evidence confirms that the JAR came from the domain; it does not show that ok.bat itself was delivered there.
The downloaded JAR has SHA-256
cfefa3ed12710aa5680ac739373a17a4637f1cd4bb06a8f1036ff9e5eff67106.
Its process chain builds the m parameter from hostname and timestamp, calls the /?m= endpoint, and uploads a local temporary text file using multipart POST. The GET pattern supports victim registration or heartbeat, while the POST supports reconnaissance-data exfiltration. Together they confirm a node serving both payload distribution and C2-related functions.
clouds.zip → Python-Packaged Executables
The two clouds.zip variants have SHA-256 19e13866627f3cd1b4cd0f9aac4945dd79605860f69c4396b70d8941fcaa986e and 84ad73535fd49de3ba36a2ceb4c865a8769749963cd327956e89cb4af95eba36.
Both are roughly 12 MB, contain PE files, and display long sleeps, user-input checks, or debugger-environment detection associated with sandbox evasion.
The first branch bundles qvmsrb.exe, SHA-256
be0ebf760d550af033fe5a1da3c081262bd2e78f9b1f0e5778ccbf030a553dc3.
The second branch is associated with a0b6ioc2.exe, SHA-256
d2e5d7669524473686efd5efbdcdd84463b7328ace122951fc76ab4c52cd2298.
Both executables are approximately 12 MB, drop runtime components typical of Python packaging, and overlap across TLSH, SSDEEP, and IMPHASH, supporting multi-version tracking as one build family.
Remote Channel and Disguised Archive Components
vpn.zip has SHA-256
bd55b1bc446855f1508e8a243f84163e12eed10ab01caa45c3f919b5863f8de4.
The archive contains PE files, carries persistence, long-sleep, and debugger-environment detection tags, and shows SoftEther VPN-related characteristics consistent with PLUMP SPIDER’s reported use of covert remote channels.
13Ex_zn.tar has SHA-256
16e61ac280757714bd4ada0fa0078bd8053c22db1f8034c157621f8b7b4cff48.
Despite its .tar extension, the file is a protected Win32 executable. The disagreement between archive-like naming and the actual PE type is a direct, high-value detection feature for mail gateways, download inspection, and endpoint controls.
| Core IOC | Position in the chain | Defensive use |
| aut-bank[.]com | JavaUpdate.jar source and /?m= GET/POST data endpoint. | Hunt for certutil downloads, SYSTEM startup tasks, hostname/timestamp parameters, and multipart uploads. |
| 151.243.219[.]89 | Historical hosting node for the first infrastructure set. | Find co-resolving domains, TLS sessions, and file downloads in the same period. |
| 24.152.36[.]138 | Hub for the second domain and payload relationship set. | Connect randomized domains, archive delivery, and remote-channel activity. |
| nuvem[.]host rickcooder[.]nuvem[.]host |
Follow-on destinations after environment checks by Python-packaged samples. | Detect the ordered sequence of an api.ipify query followed by these connections. |
Attack Chain and MITRE ATT&CK Mapping
| Stage | Observed Behavior or Risk | MITRE ATT&CK Reference | Defender Focus |
| Trust building | Impersonated support through messaging or voice. | T1566.004 — Spearphishing Voice T1566.003 — Spearphishing via Service |
Verified channels, tickets, and callbacks. |
| User execution | A reconnaissance script runs behind a disguised extension. | T1204.002 — Malicious File T1059.001 — PowerShell |
True file type, process lineage, and script logs. |
| Discovery | Host, domain, DNS, network, and controller data are queried. | T1082 — System Information Discovery T1016 — System Network Configuration Discovery T1482 — Domain Trust Discovery |
Clustered queries and unusual execution identity. |
| Command and control | Structured JSON is sent to external C2. | T1071.001 — Web Protocols T1041 — Exfiltration Over C2 Channel |
Script-process egress and small structured transfers. |
| Persistence and expansion | Remote access, tunneling, directory mapping, and lateral exploration. | T1219.002 — Remote Desktop Software T1572 — Protocol Tunneling T1087.002 — Domain Account |
New services, adapters, enumeration, and first gateway access. |
| Payment fraud | Fraudulent payment instructions are generated, signed, and submitted. | Not fully represented by MITRE ATT&CK | Transaction context, HSM calls, and settlement anomalies. |
Recommended Actions
- Preserve evidence before removing access: Isolate suspicious endpoints and maintenance sessions while retaining script, process, network, identity, and payment records.
- Rotate the full reachable credential set from clean systems: Include employee, supplier, remote-access, service-account, gateway-management, and signing identities.
- Make IT support independently verifiable: Require every update and remote-assistance request to map to a searchable ticket and a known callback path.
- Constrain scripts and remote access: Apply allowlists, time-bound approval, change windows, and least privilege to interpreters, remote services, tunnels, and relays.
- Segment payment gateways from office and support networks: Deny default reachability and revalidate identity and device posture at every hop.
- Bind signing to transaction context: Use separation of duties, dual control, velocity and amount limits, and traceability from every HSM call to the original order and approval.
- Track infrastructure change continuously: Monitor time-bounded DNS, certificates, similar samples, and randomized domains using multi-evidence scoring rather than broad cloud or ASN blocks.
How Sangfor Helps
| Pain Point | Sangfor Solution |
| Attackers bypassing traditional firewalls via encrypted C2 tunnels and hijacked domains (.gov.br). | Athena SASE Enforces strict Zero Trust Network Access policies, ensuring that authentication alone never grants blanket internal network access. Inspects encrypted traffic channels and blocks unauthorized external connections or suspicious domain communications, neutralizing the perimeter bypass phase before credentials can be harvested. |
| Credential theft, lateral movement, and forged pacs.008 transactions that mimic legitimate traffic. | Athena XDR Identity & Operation Linkage: Automatically correlates endpoint privilege escalation events (such as Windows Event 4672) with API request behaviors directed at the Pix Gateway. Application-Layer Anomaly Detection: Monitors transaction metrics beyond basic protocol validity—analyzing sudden shifts in pacs.008 signing frequencies, single-transaction amount anomalies, and execution timing deviations to flag credential abuse instantly. |
| Advanced, multi-stage APT campaigns leaving behind flawless, "compliant" logs that evade automated rules. | Athena MDR Human-Led Threat Hunting: Combines AI-driven detection with elite security analysts to hunt for stealthy, fileless persistence mechanisms (ok.bat, scheduled tasks) and subtle lateral movement patterns. Deep Contextual Investigation: Validates complex financial and cryptographic transaction workflows to uncover sophisticated intrusions where automated compliance engines fail to spot unauthorized intent. |
Call to Action
If your organization operates a real-time payment gateway, provides technology to multiple financial institutions, or permits third-party maintenance of critical systems, begin with an end-to-end trust review: who can initiate support, who can execute updates, which identities can cross network boundaries, which application can request a signature, and whether every signature can be traced back to legitimate business authorization.
Even if these IOCs are absent from your environment, treat PLUMP SPIDER as a realistic rehearsal. Domains and hashes will change; the logic is reusable: entering through support trust, mapping the environment to choose a path, and converting legitimate payment capability into fraud.
A payment-security response is complete only when the person, endpoint, identity, network path, gateway, signature, and transaction record have all been examined.
Source Index
- Axur Research Team, “New Details on Plump Spider’s Operations in Pix Fraud Schemes,” October 8, 2025, updated November 14, 2025. Supports the directly observed support impersonation, reconnaissance script, collected fields, post-entry TTPs, Pix Gateway behavior, and HSM signing-abuse model.
https://blog.axur.com/en-us/axur-reveals-plump-spider-modus-operandi-systemic-pix-fraud - CrowdStrike, “PLUMP SPIDER Adversary Profile.” Supports actor classification, activity period, Brazil-focused targeting, social-engineering capability, and financial-fraud objective.
https://www.crowdstrike.com/en-us/adversaries/plump-spider/ - Google Threat Intelligence Group / Mandiant, “Financially Motivated Threat Actor BREEZE COMET Targets Brazil,” September 1, 2026. Documents closely overlapping activity, including IT-support impersonation, compromised Brazilian government websites, credential and certificate hunting, and financial-system targeting.
https://cloud.google.com/blog/topics/threat-intelligence/financially-motivated-threat-actor-breeze-comet-targets-brazil - Banco Central do Brasil, “Instant Payment System (SPI)” and Pix technical documentation. Provides first-party background on Pix settlement infrastructure and instant-payment processing in Brazil.
https://www.bcb.gov.br/en/financialstability/spi_en - MITRE, “ATT&CK Enterprise Matrix.” Provides standardized technique references used in the attack-chain table.
https://attack.mitre.org/matrices/enterprise/ - VirusTotal, public domain record for aut-bank.com, retrieved September 16, 2026. Supports time-bounded review of public verdicts and relationships used alongside the FarSight Labs infrastructure investigation.
https://www.virustotal.com/gui/domain/aut-bank.com