Athena SWG supports HTTP/HTTPS, FTP, and SOCKS4/SOCKS5 proxy services, helping conceal users’ internal IP addresses from external destinations. Proxy chaining enables cascaded deployments and layered policy enforcement. Built-in web filtering enforces browsing policies and helps block malicious and phishing websites. ICAP integration with third-party antivirus and data loss prevention (DLP) solutions supports malware scanning and sensitive-data inspection.
Proxy-Based SWG for Internet and GenAI Control
Modern work depends on websites, cloud services, and generative AI (GenAI). As employees use more online tools across offices, branches, and remote locations, organizations face growing exposure to web-based threats, unmanaged application use, and the risk of sensitive information leaving the business. At the same time, overly restrictive security measures can disrupt everyday work.
Athena SWG helps organizations balance these needs. As a secure web gateway, it helps provide safe, manageable internet access and gives IT teams the visibility and control to reduce online risks, guide responsible use of web and GenAI services, and apply consistent policies across the workforce—without getting in the way of productivity.
Athena SWG Use Cases
As employees increasingly rely on web applications and GenAI tools, managing internet usage across offices and branches has become more challenging. Bandwidth-intensive activities such as video streaming can affect business-critical applications, while uncontrolled GenAI usage may expose sensitive company information. IT teams need to balance employee productivity with effective oversight of internet resources and online activities.Athena SWG helps organizations manage office internet and GenAI usage through consistent access policies, application bandwidth prioritization, and visibility into user activities. This enables IT teams to maintain reliable access to business applications, manage potential GenAI-related risks, and enforce consistent internet usage policies across locations without unnecessarily restricting employee productivity.
Because customers have vastly different authentication procedures, each internal network requires user authentication integration with AD, Radius to achieve SSO. Athena SWG guest authentication provides convenient access through Facebook, WeChat, SMS and offers a unified authentication solution, which manages both the wired and wireless connected users within a single SWG platform. Athena SWG also offers a switch based user access control capability to help control LAN user access. Finally, Sangfor SWG can be integrated with WLAN vendors like Cisco, Aruba to allow the Unified Authentication Center to drastically simplify the process of network integration and management.
Everyday web browsing can expose employees to phishing, malware, and other internet-borne threats, while the use of online services can increase the risk of sensitive-data leakage. Encrypted web traffic makes some threats harder to detect, and organizations need effective protection that works with their existing network and security infrastructure.Athena SWG helps organizations secure employee internet access through web filtering, proxy-based traffic control, and inspection of supported encrypted traffic. Its ICAP integration enables organizations to extend protection using existing antivirus and DLP solutions, helping reduce exposure to web threats and sensitive-data leakage while maintaining consistent security policies.
As unauthorized use of networks becomes more common, many countries and regions are developing and enforcing laws governing user internet access behavior. The Athena SWG internal application database comprehensively logs malicious user activity including file uploads, BBS posting, email, browsing history, and applications accessed. This audit solution assists in customer compliance with local legal regulations and serves as a valuable investigative resource in the event of illegal network usage incidents.
Why Choose Sangfor Athena SWG?
Athena SWG enables you to identify, analyze and take immediate action upon user internet access behavior
Industry & Market Recognition
Gartner Magic Quadrant for Secure Web Gateways: 10 consecutive years (2011–2020).
Listed as a Sample Vendor for SWG in Gartner Hype Cycle.
No. 1 SWG market share in Indonesia, Thailand, and Hong Kong in 2025 (Gartner, Market Share: Security Software, Worldwide, 2025).
Local Support & Better Services
Local Sangfor offices and technical support teams.
Ongoing investment in proxy-based SWG R&D, with rapid response from the R&D team.
Differentiating Features
Patented P2P and dynamic bandwidth control technology.
A practical replacement for existing SWG solutions, with support for multiple ICAP integrations.
2,600+ AI signatures for 10+ AI agent tools.
Large Customer Base
Leading banks and enterprises across Malaysia, Hong Kong, and Indonesia.
Government agencies and top-20 universities in Malaysia, Indonesia, and Thailand.
Over 400 banks and large enterprises in mainland China, including BYD, ICBC, CCB, BOC, and ABC.
Athena SWG Key Features and Capabilities
Proxy & ICAP Services
Intelligent Traffic Management
Athena SWG improves bandwidth utilization by more than 30% using three unique major traffic management solutions. Dynamic Traffic Control automatically adjusts traffic control policies and intelligently allocates idle bandwidth resources. Intelligent Flow Control precisely manages both up-link and down-link P2P traffic and can customize traffic "packages" for different users, allocating specific traffic quotas and limiting bandwidth for heavier users.
Gateway- & Client-Based Decryption
Athena SWG supports both gateway-based and client-based SSL/TLS decryption to enable security inspection of encrypted web traffic. Either method can be deployed independently, or both can run in parallel, depending on organizational security policies and IT requirements.
Unified Authentication Platform
Athena SWG provides centralized authentication for employees, partners, and guests across wired and wireless networks. It supports 29 authentication methods, including single sign-on (SSO) with Active Directory (AD), username/password, IP/MAC binding, QR codes, SMS, WeChat, social login, OA accounts, SAML 2.0, and third-party integrations.
Administrators can define access permissions by user, application, location, and device type. Integration with compatible wireless controllers supports unified authentication and network-wide access management.
GenAI & Granular Application Control
Athena SWG provides granular application and GenAI control through Asia’s largest application signature database, which identifies 6,000+ applications—including 700+ cloud, 1,000+ mobile, and 300+ web applications—and is updated every two weeks. It also includes 2,600+ AI signatures covering ChatGPT, Gemini, Claude, and Chinese AI applications.
For supported GenAI services, administrators can review application usage, prompts, responses, and file activity and apply policies to uploads, downloads, and social posts. Policies can also restrict Microsoft Office access to enterprise accounts. Bulk policy management and application-aware bandwidth allocation support efficient administration and traffic prioritization.
Secure Onboarding Devices With Endpoint Security Posture
Athena SWG identifies and secure endpoint devices with or without agents, it helps to ensure these devices are connected with compliant and secure. You gain visibility and control what is on your environment without impacting your network performance.
Secure Device Onboarding with NAC
Athena SWG uses agent-based network access control (NAC) to identify endpoint devices and check compliance with access requirements. Its Ingress Client policies can evaluate device attributes such as login domain, operating system, processes, files, registry entries, scheduled tasks, patches, installed software, Windows accounts, and external device controls. Checks can also cover antivirus and anti-defacement software, including their update and signature database versions, to support secure device onboarding.
Proxy & ICAP Services
Athena SWG supports HTTP/HTTPS, FTP, and SOCKS4/SOCKS5 proxy services, helping conceal users’ internal IP addresses from external destinations. Proxy chaining enables cascaded deployments and layered policy enforcement. Built-in web filtering enforces browsing policies and helps block malicious and phishing websites. ICAP integration with third-party antivirus and data loss prevention (DLP) solutions supports malware scanning and sensitive-data inspection.
Intelligent Traffic Management
Athena SWG improves bandwidth utilization by more than 30% using three unique major traffic management solutions. Dynamic Traffic Control automatically adjusts traffic control policies and intelligently allocates idle bandwidth resources. Intelligent Flow Control precisely manages both up-link and down-link P2P traffic and can customize traffic "packages" for different users, allocating specific traffic quotas and limiting bandwidth for heavier users.
Gateway- & Client-Based Decryption
Athena SWG supports both gateway-based and client-based SSL/TLS decryption to enable security inspection of encrypted web traffic. Either method can be deployed independently, or both can run in parallel, depending on organizational security policies and IT requirements.
Unified Authentication Platform
Athena SWG provides centralized authentication for employees, partners, and guests across wired and wireless networks. It supports 29 authentication methods, including single sign-on (SSO) with Active Directory (AD), username/password, IP/MAC binding, QR codes, SMS, WeChat, social login, OA accounts, SAML 2.0, and third-party integrations.
Administrators can define access permissions by user, application, location, and device type. Integration with compatible wireless controllers supports unified authentication and network-wide access management.
GenAI & Granular Application Control
Athena SWG provides granular application and GenAI control through Asia’s largest application signature database, which identifies 6,000+ applications—including 700+ cloud, 1,000+ mobile, and 300+ web applications—and is updated every two weeks. It also includes 2,600+ AI signatures covering ChatGPT, Gemini, Claude, and Chinese AI applications.
For supported GenAI services, administrators can review application usage, prompts, responses, and file activity and apply policies to uploads, downloads, and social posts. Policies can also restrict Microsoft Office access to enterprise accounts. Bulk policy management and application-aware bandwidth allocation support efficient administration and traffic prioritization.
Secure Onboarding Devices With Endpoint Security Posture
Athena SWG identifies and secure endpoint devices with or without agents, it helps to ensure these devices are connected with compliant and secure. You gain visibility and control what is on your environment without impacting your network performance.
Secure Device Onboarding with NAC
Athena SWG uses agent-based network access control (NAC) to identify endpoint devices and check compliance with access requirements. Its Ingress Client policies can evaluate device attributes such as login domain, operating system, processes, files, registry entries, scheduled tasks, patches, installed software, Windows accounts, and external device controls. Checks can also cover antivirus and anti-defacement software, including their update and signature database versions, to support secure device onboarding.

Partner Success with Sangfor: Global Sapphire's Growth Partnership & Development
Partner Success with Sangfor: Global Sapphire's Growth Partnership & Development

Customer Success with Sangfor: EBM Enhances IT Infrastructure and Support
Unveiling IT Transformation at PT. CJ Indonesia | Sangfor Tech Talk
Innovation and Success: Sangfor x Universitas Pelita Harapan's Story
Interview with IBA Karachi's Head of ICT Wajeeh Zaidi - Customer Testimonial
Interview with Shahid Khan Jadoon, Manager IT | National Information Technology Board NITB, Pakistan
Ramsay Sime Darby Healthcare x Sangfor: Success Story
PT Bank Victoria International Tbk x Sangfor: Success Story
| Models | M5100 | M5200 | M5400 | M5500 | M5600 | M6000 | M6000-UPG¹ | M9000 | M10000 | M12000 | M14000 | M5500-SK | M5800-SK |
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| Profile | 1U | 1U | 1U | 1U | 1U | 2U | 2U | 2U | 2U | 2U | 2U | 1U | 1U |
| HD Capacity | 256 GB SSD | 128 GB SSD + 960 GB SSD | 128 GB SSD + 960 GB SSD | 128 GB SSD + 960 GB SSD | 128 GB SSD + 960 GB SSD | 128 GB SSD + 960 GB SSD | 128 GB SSD + 960 GB SSD | 480 GB SSD + 960 GB SSD | 480 GB SSD + 960 GB SSD | 480 GB SSD + 960 GB SSD | 480 GB SSD + 1.92 TB SSD | 128 GB MSATA | 128 GB MSATA + 480 GB SSD |
| Application Layer Throughput Options | 160 Mbps | 400 Mbps | 600 Mbps | 1 Gbps | 1.2 Gbps | 2 Gbps | 4 Gbps | 10 Gbps | 20 Gbps | 40 Gbps | 60 Gbps (Bypass) / 50Gbps (Bridge) | 750 Mbps | 1.5 Gbps |
| Recommended Concurrent Users | 600 Users | 2,000 Users | 3,000 Users | 5,000 Users | 6,000 Users | 15,000 Users | 20,000 Users | 50,000 Users | 100,000 Users | 200,000 Users | 200,000 Users | 1,000 Users | 2,000 Users |
| Model Datasheets Click to Download |  | | | | | | | | | | | | |
¹ M6000-UPG is a license upgrade from M6000 with application layer bandwidth increased from 1G to 2G.
Secure Internet Gateway Frequently Asked Questions
Please perform it following:
- Step 1. Add a new LDAP Server under the External Auth Server.
- Step 2. Enter the details such as Server Name, IP Address of the external authentication server, the admin account username and password and select the BaseDN. After entered all the details, click the Test Validity to check whether able to connect the external authentication server or not.
- Step 3. After tested the validity, a message will prompt out to show the result.
- Step 4. Click the Sync with all LDAP servers to sync all the data. Now, the configuration is successfully set.
In a typical environment, Secure Web Gateway (SWG) is used to block access to inappropriate websites or applications, prevent malware infections, and enforce corporate internet compliance. SWG is similar to a firewall in that both prevent malicious activities and provide necessary network security protections. However, the main difference is that SWG emphasizes securing user onboarding and promoting productivity. It is common for an enterprise to use both SWG and firewall to fortify their defense as both of them usually complement each other. For more info on using both Athena SWG and Athena NGFW, please refer to this blog webpage.
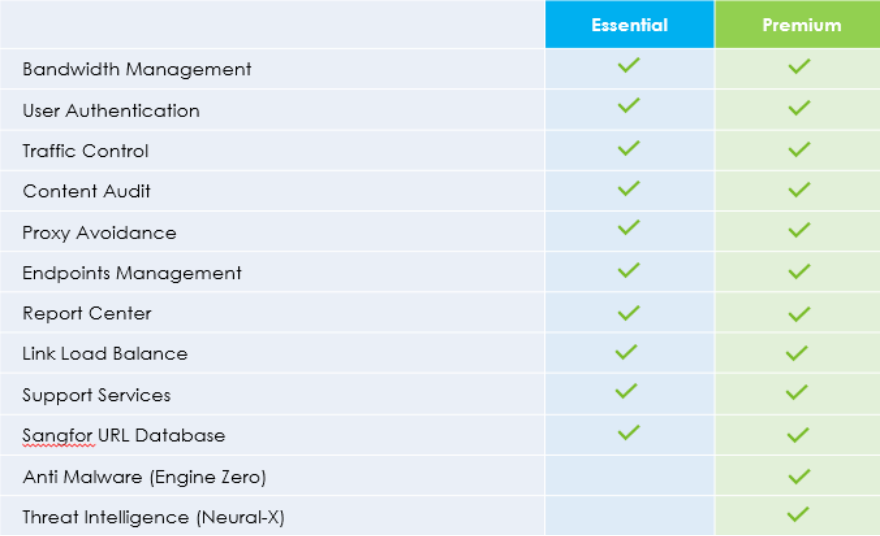
The main difference is Premium Bundle will have all the Essential Bundle components with the addition of Anti-malware protection (Engine Zero) and threat intelligence (Neural-X).