The Hidden Risk in the Trusted Update
Trusted software updates are supposed to reduce risk.
In targeted supply chain abuse, that same trust can become the delivery path.
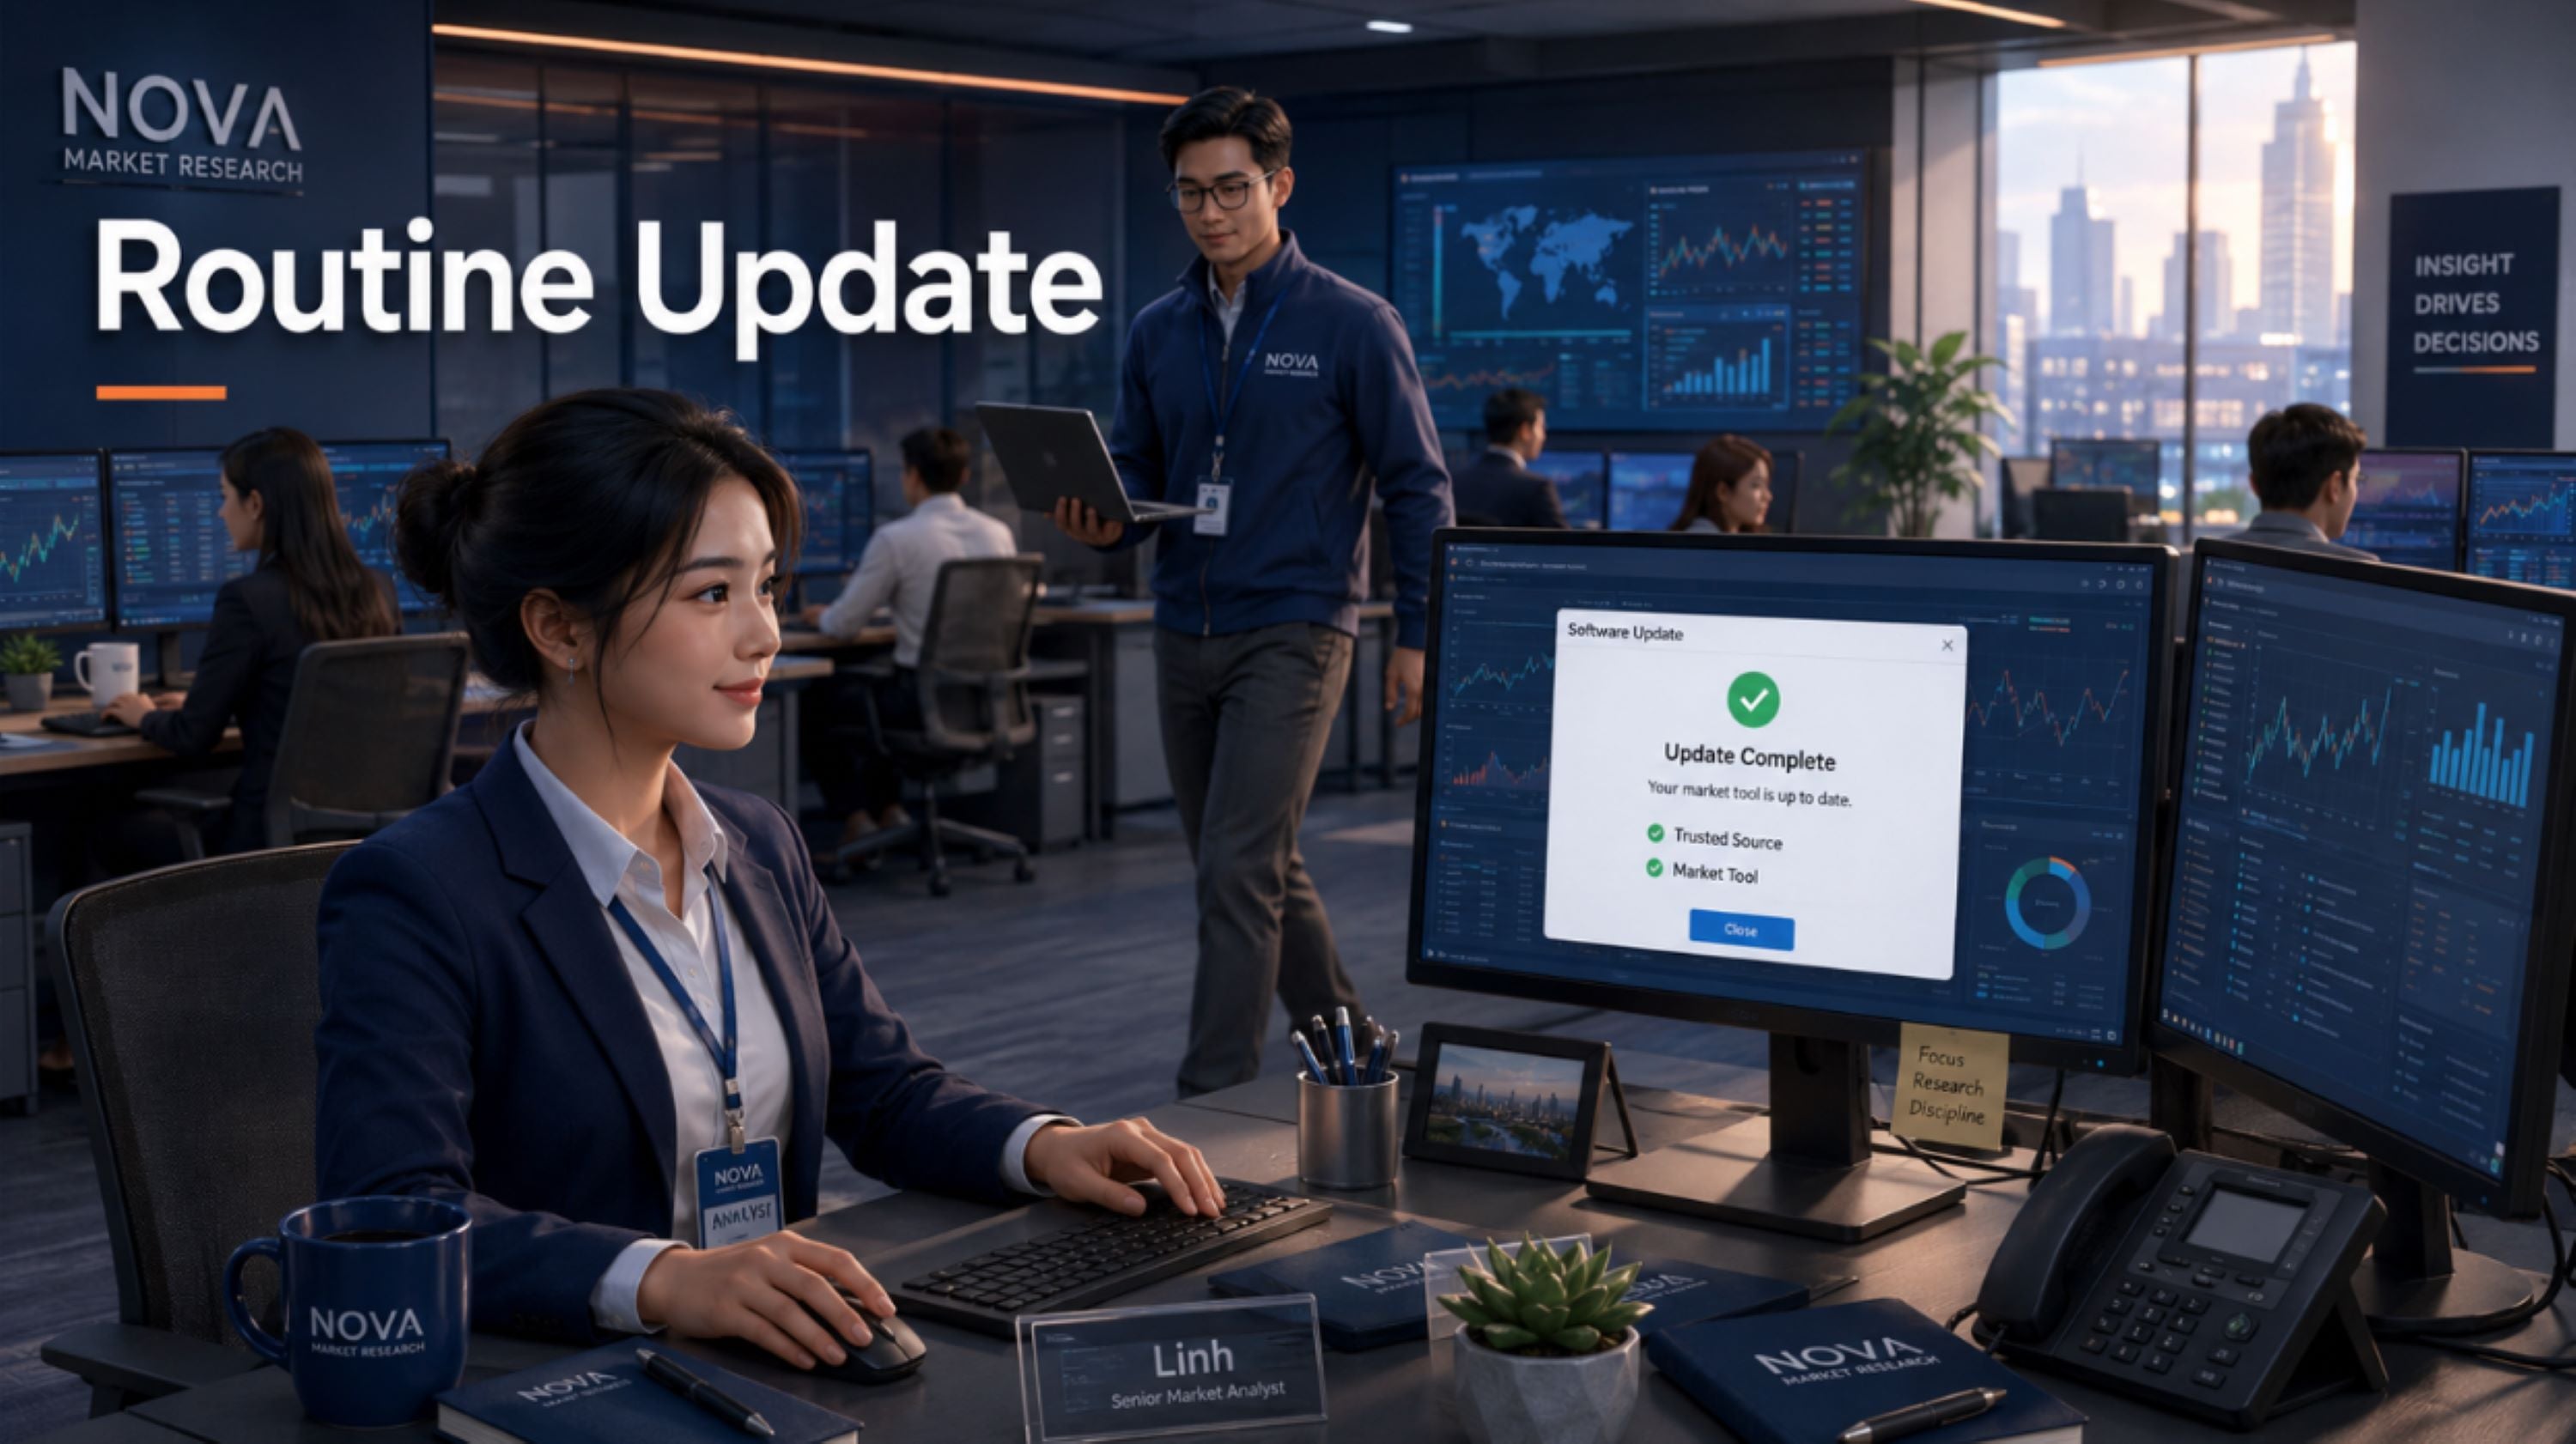
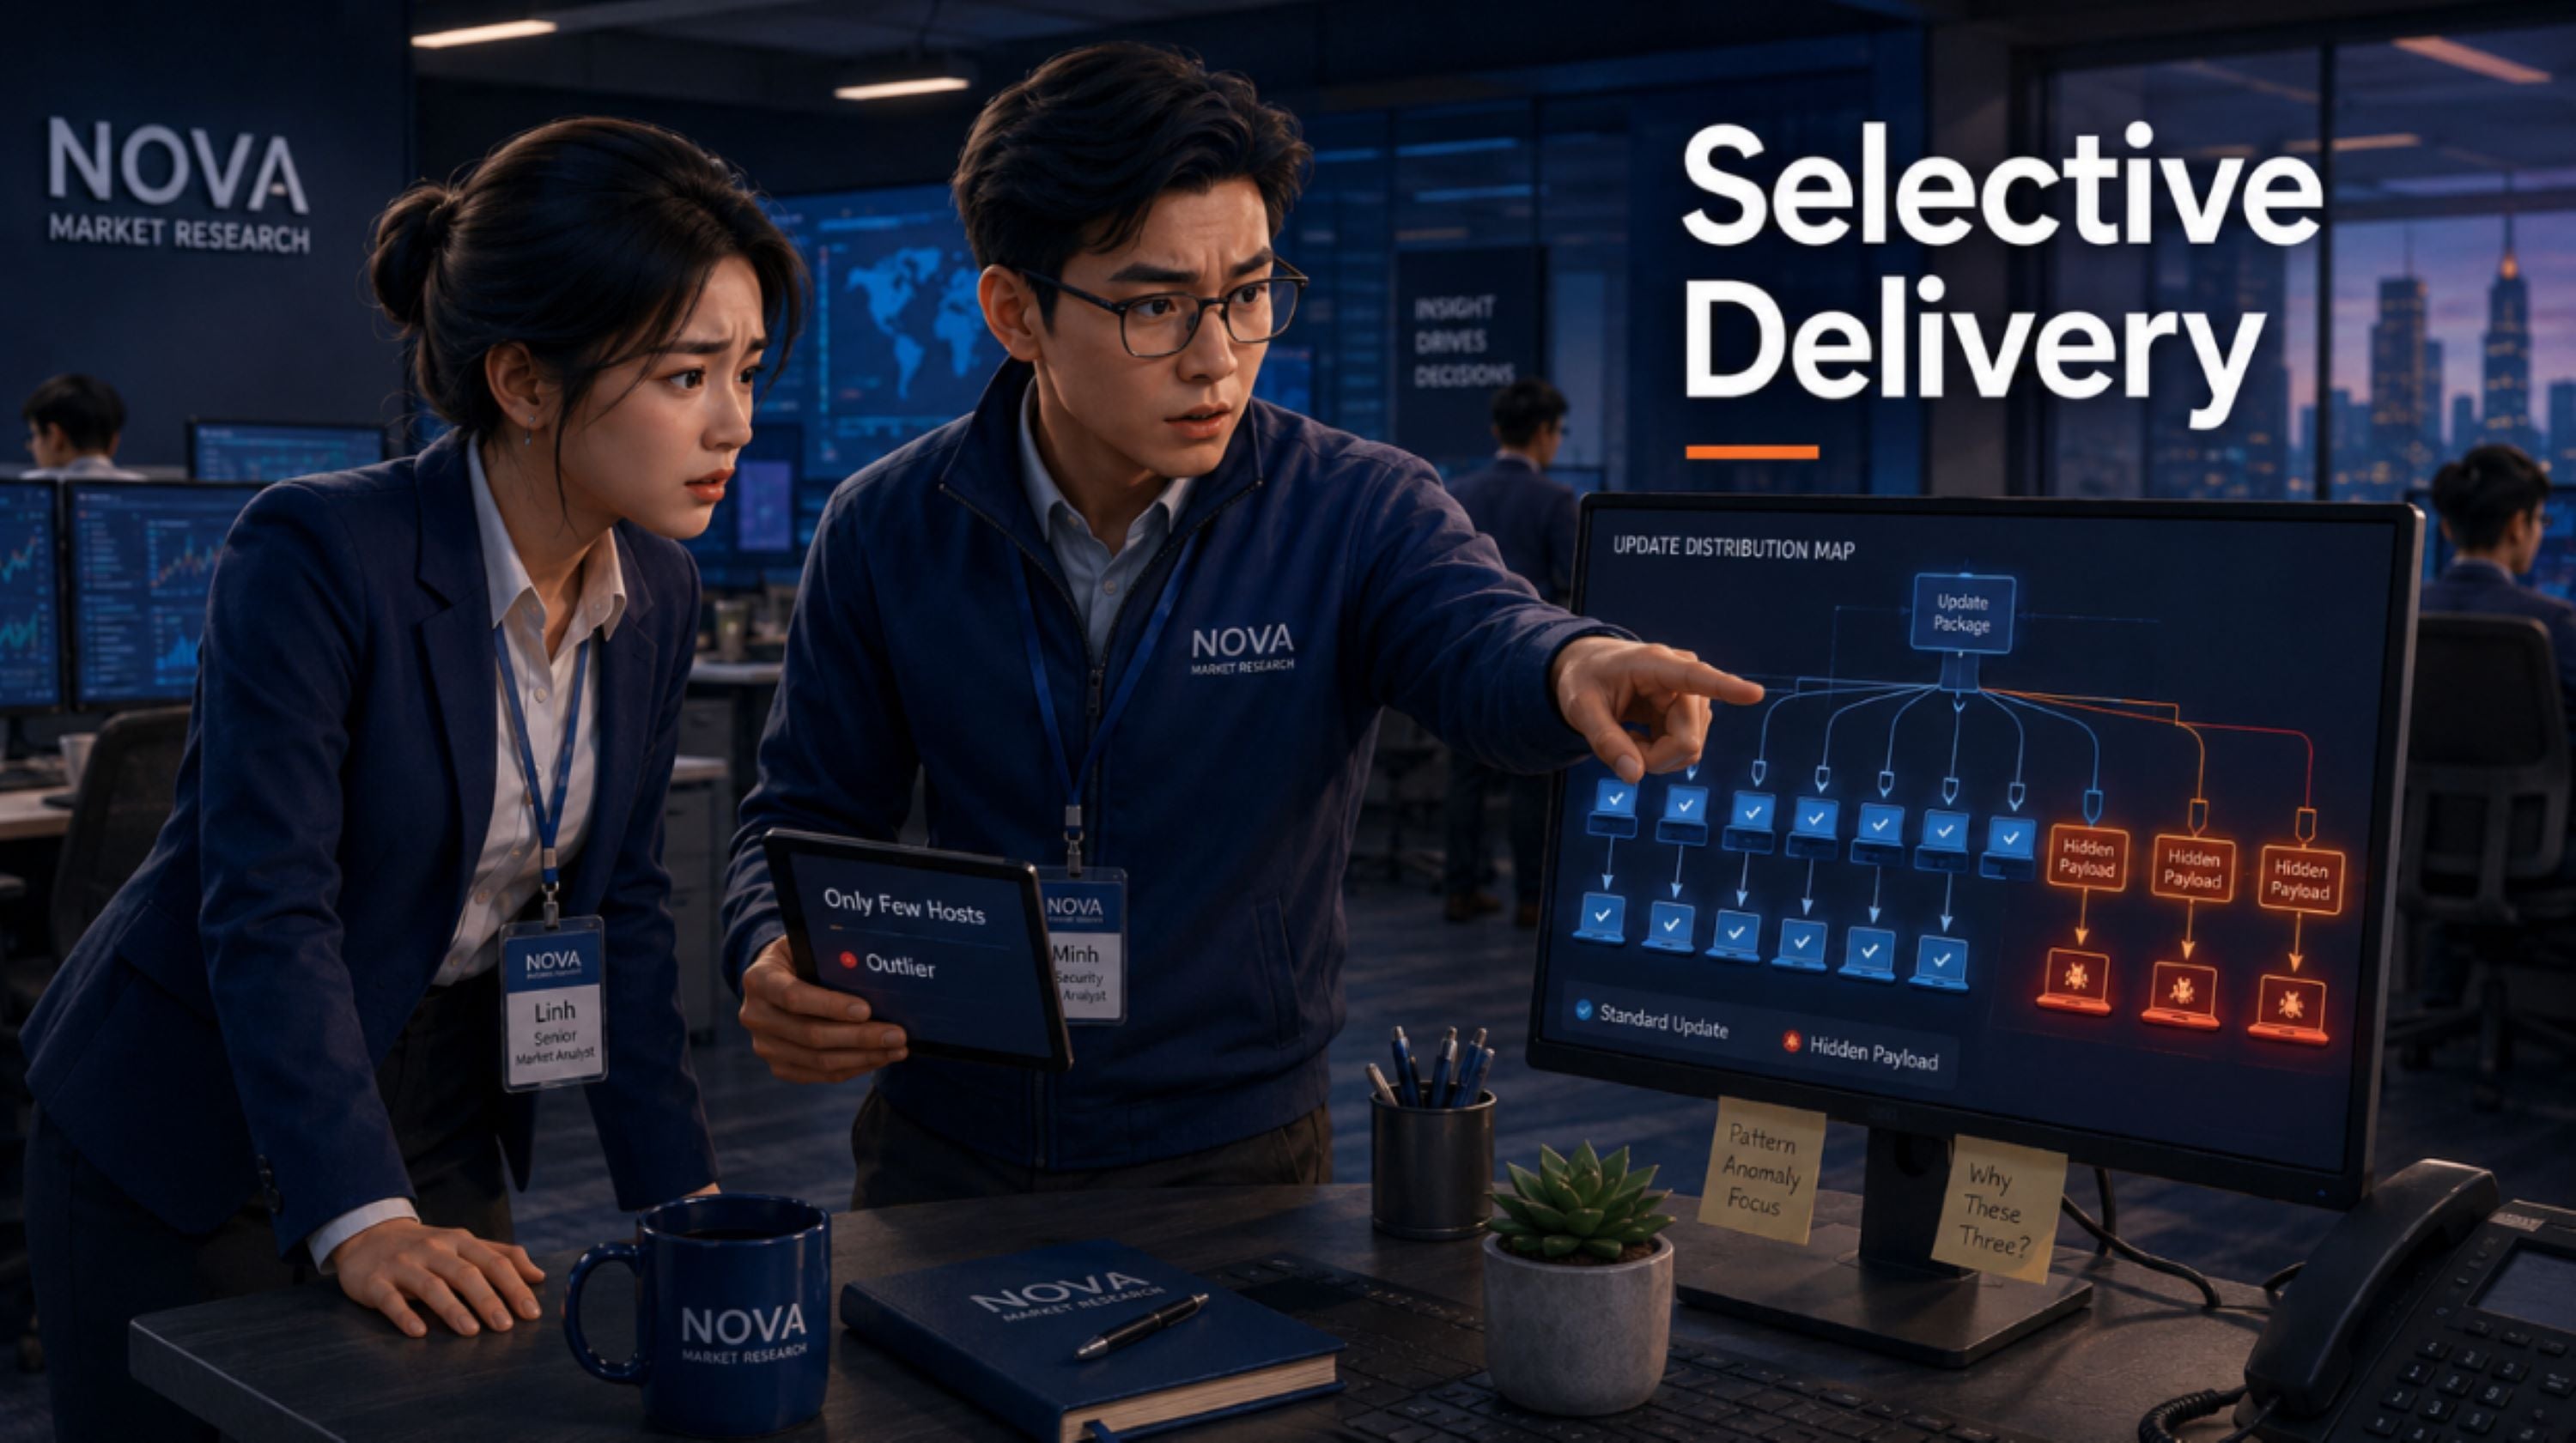
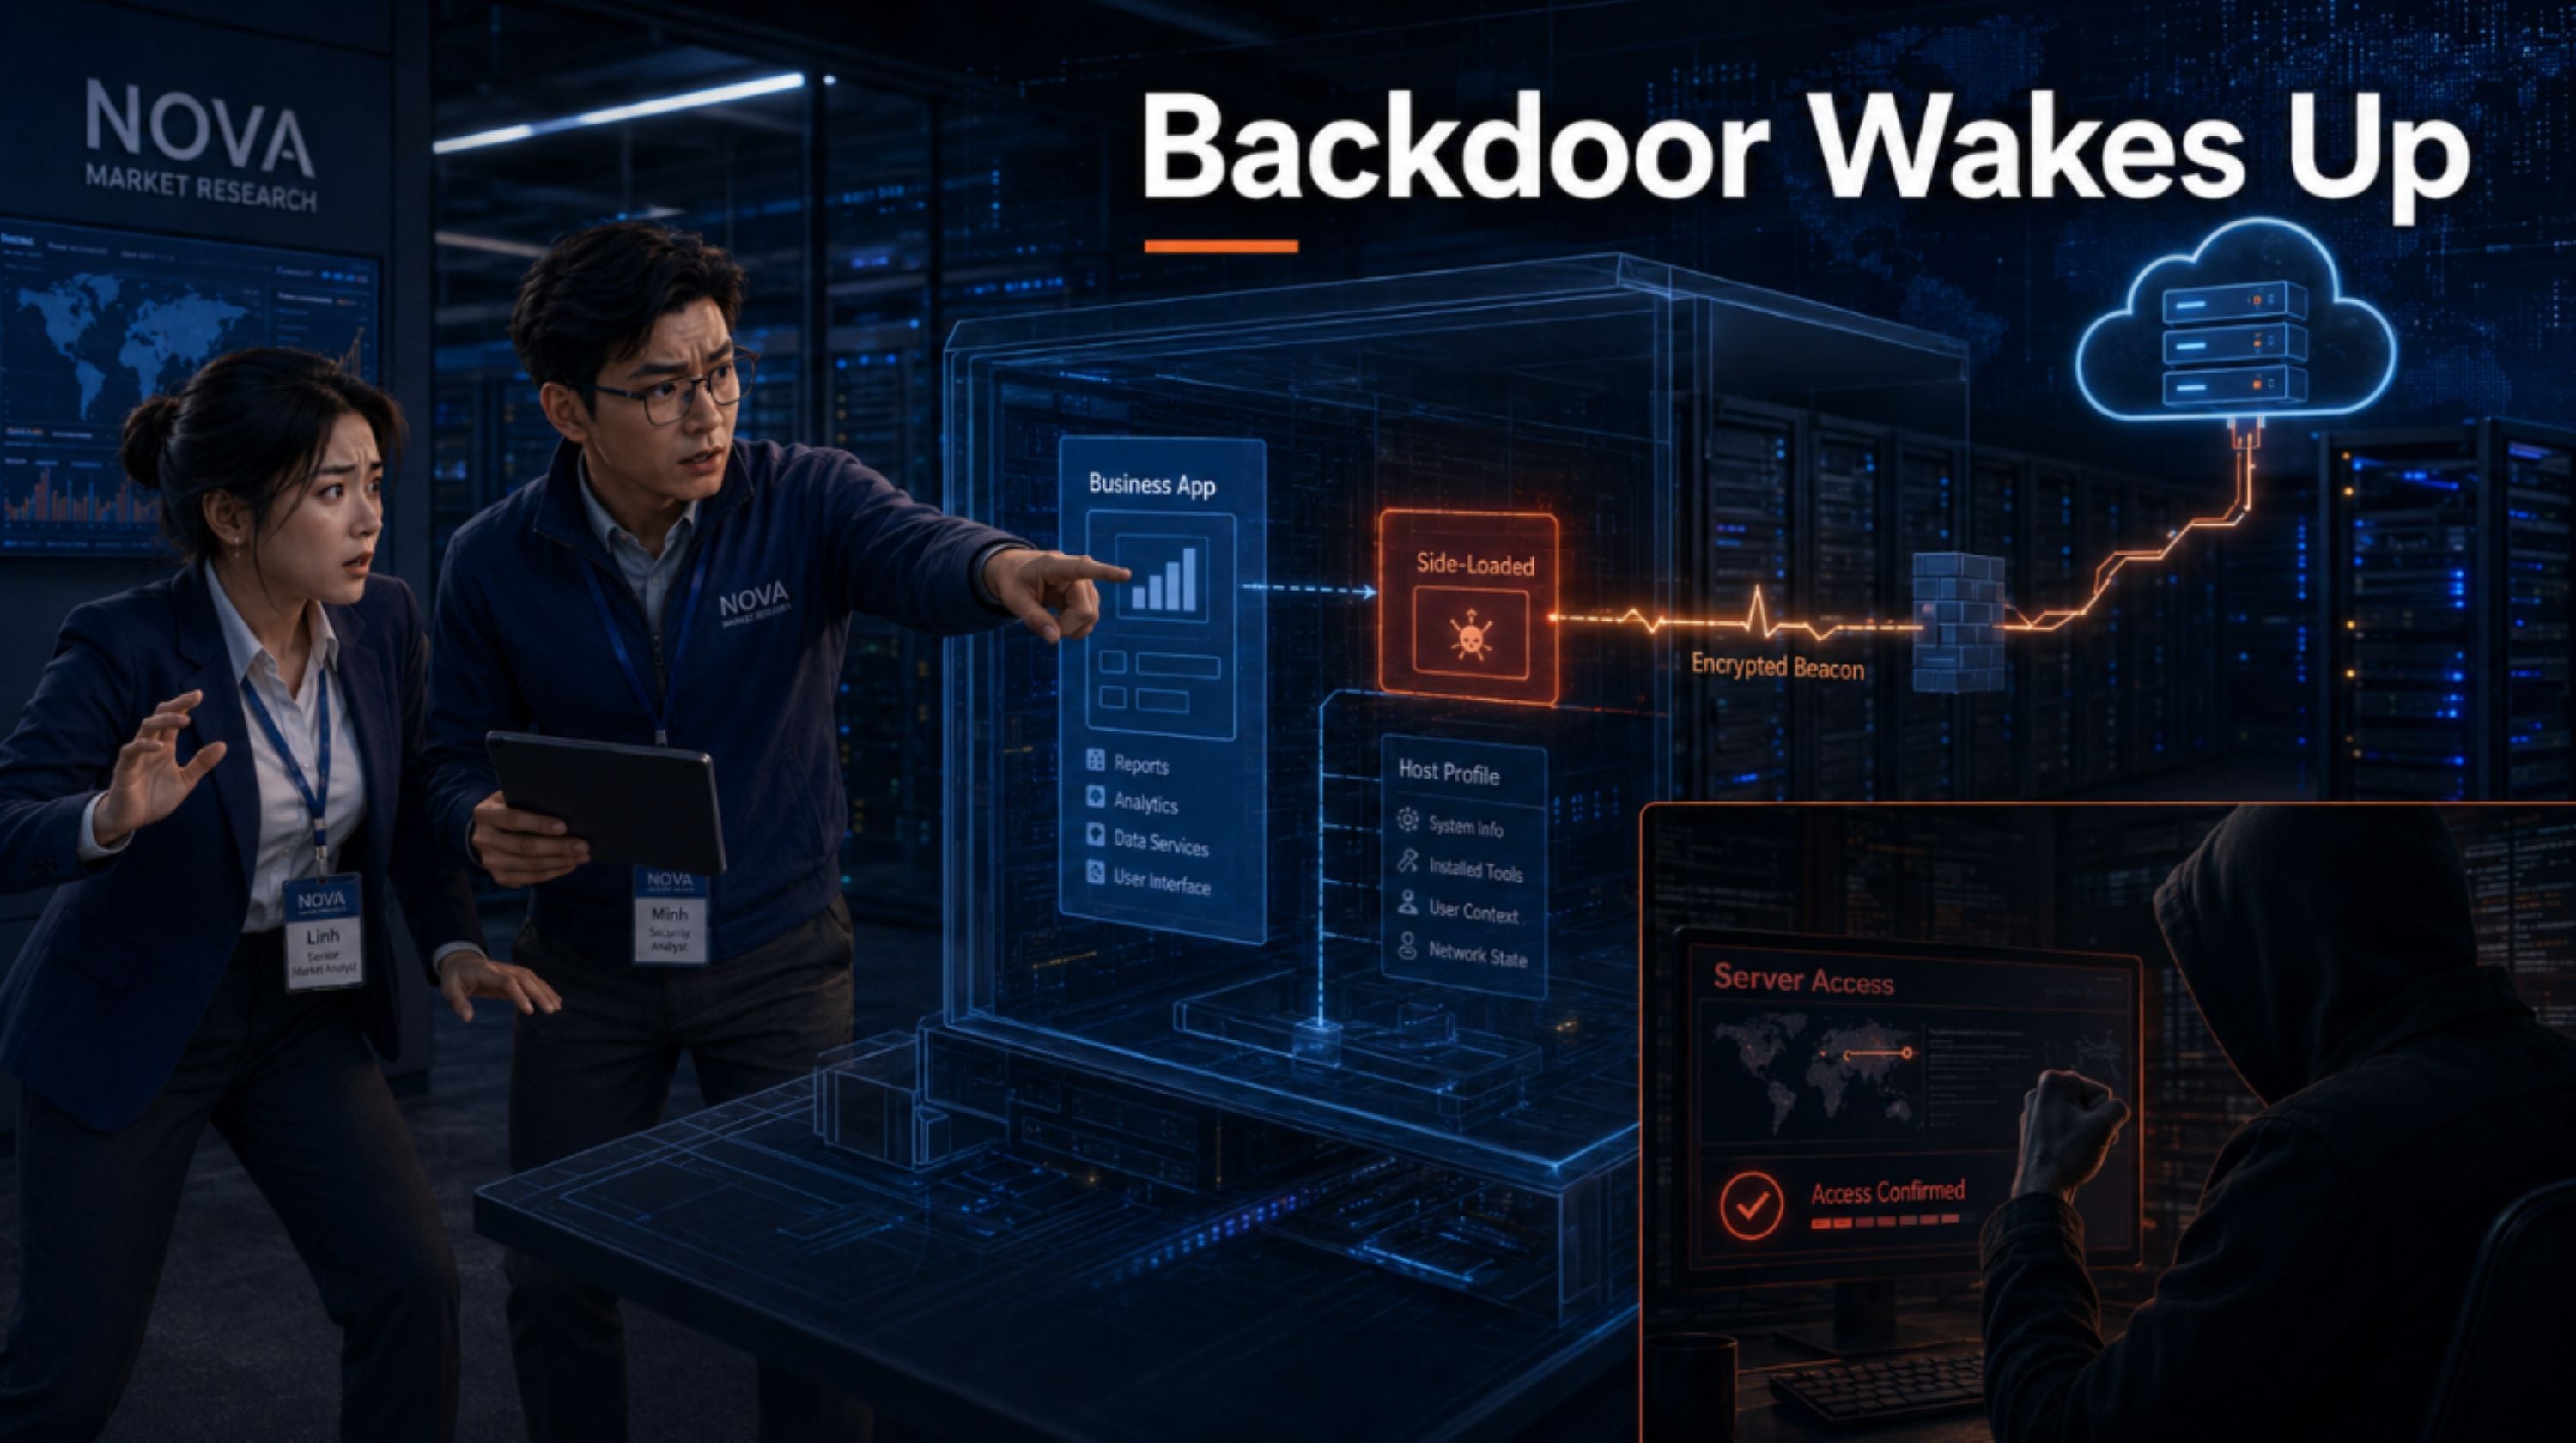
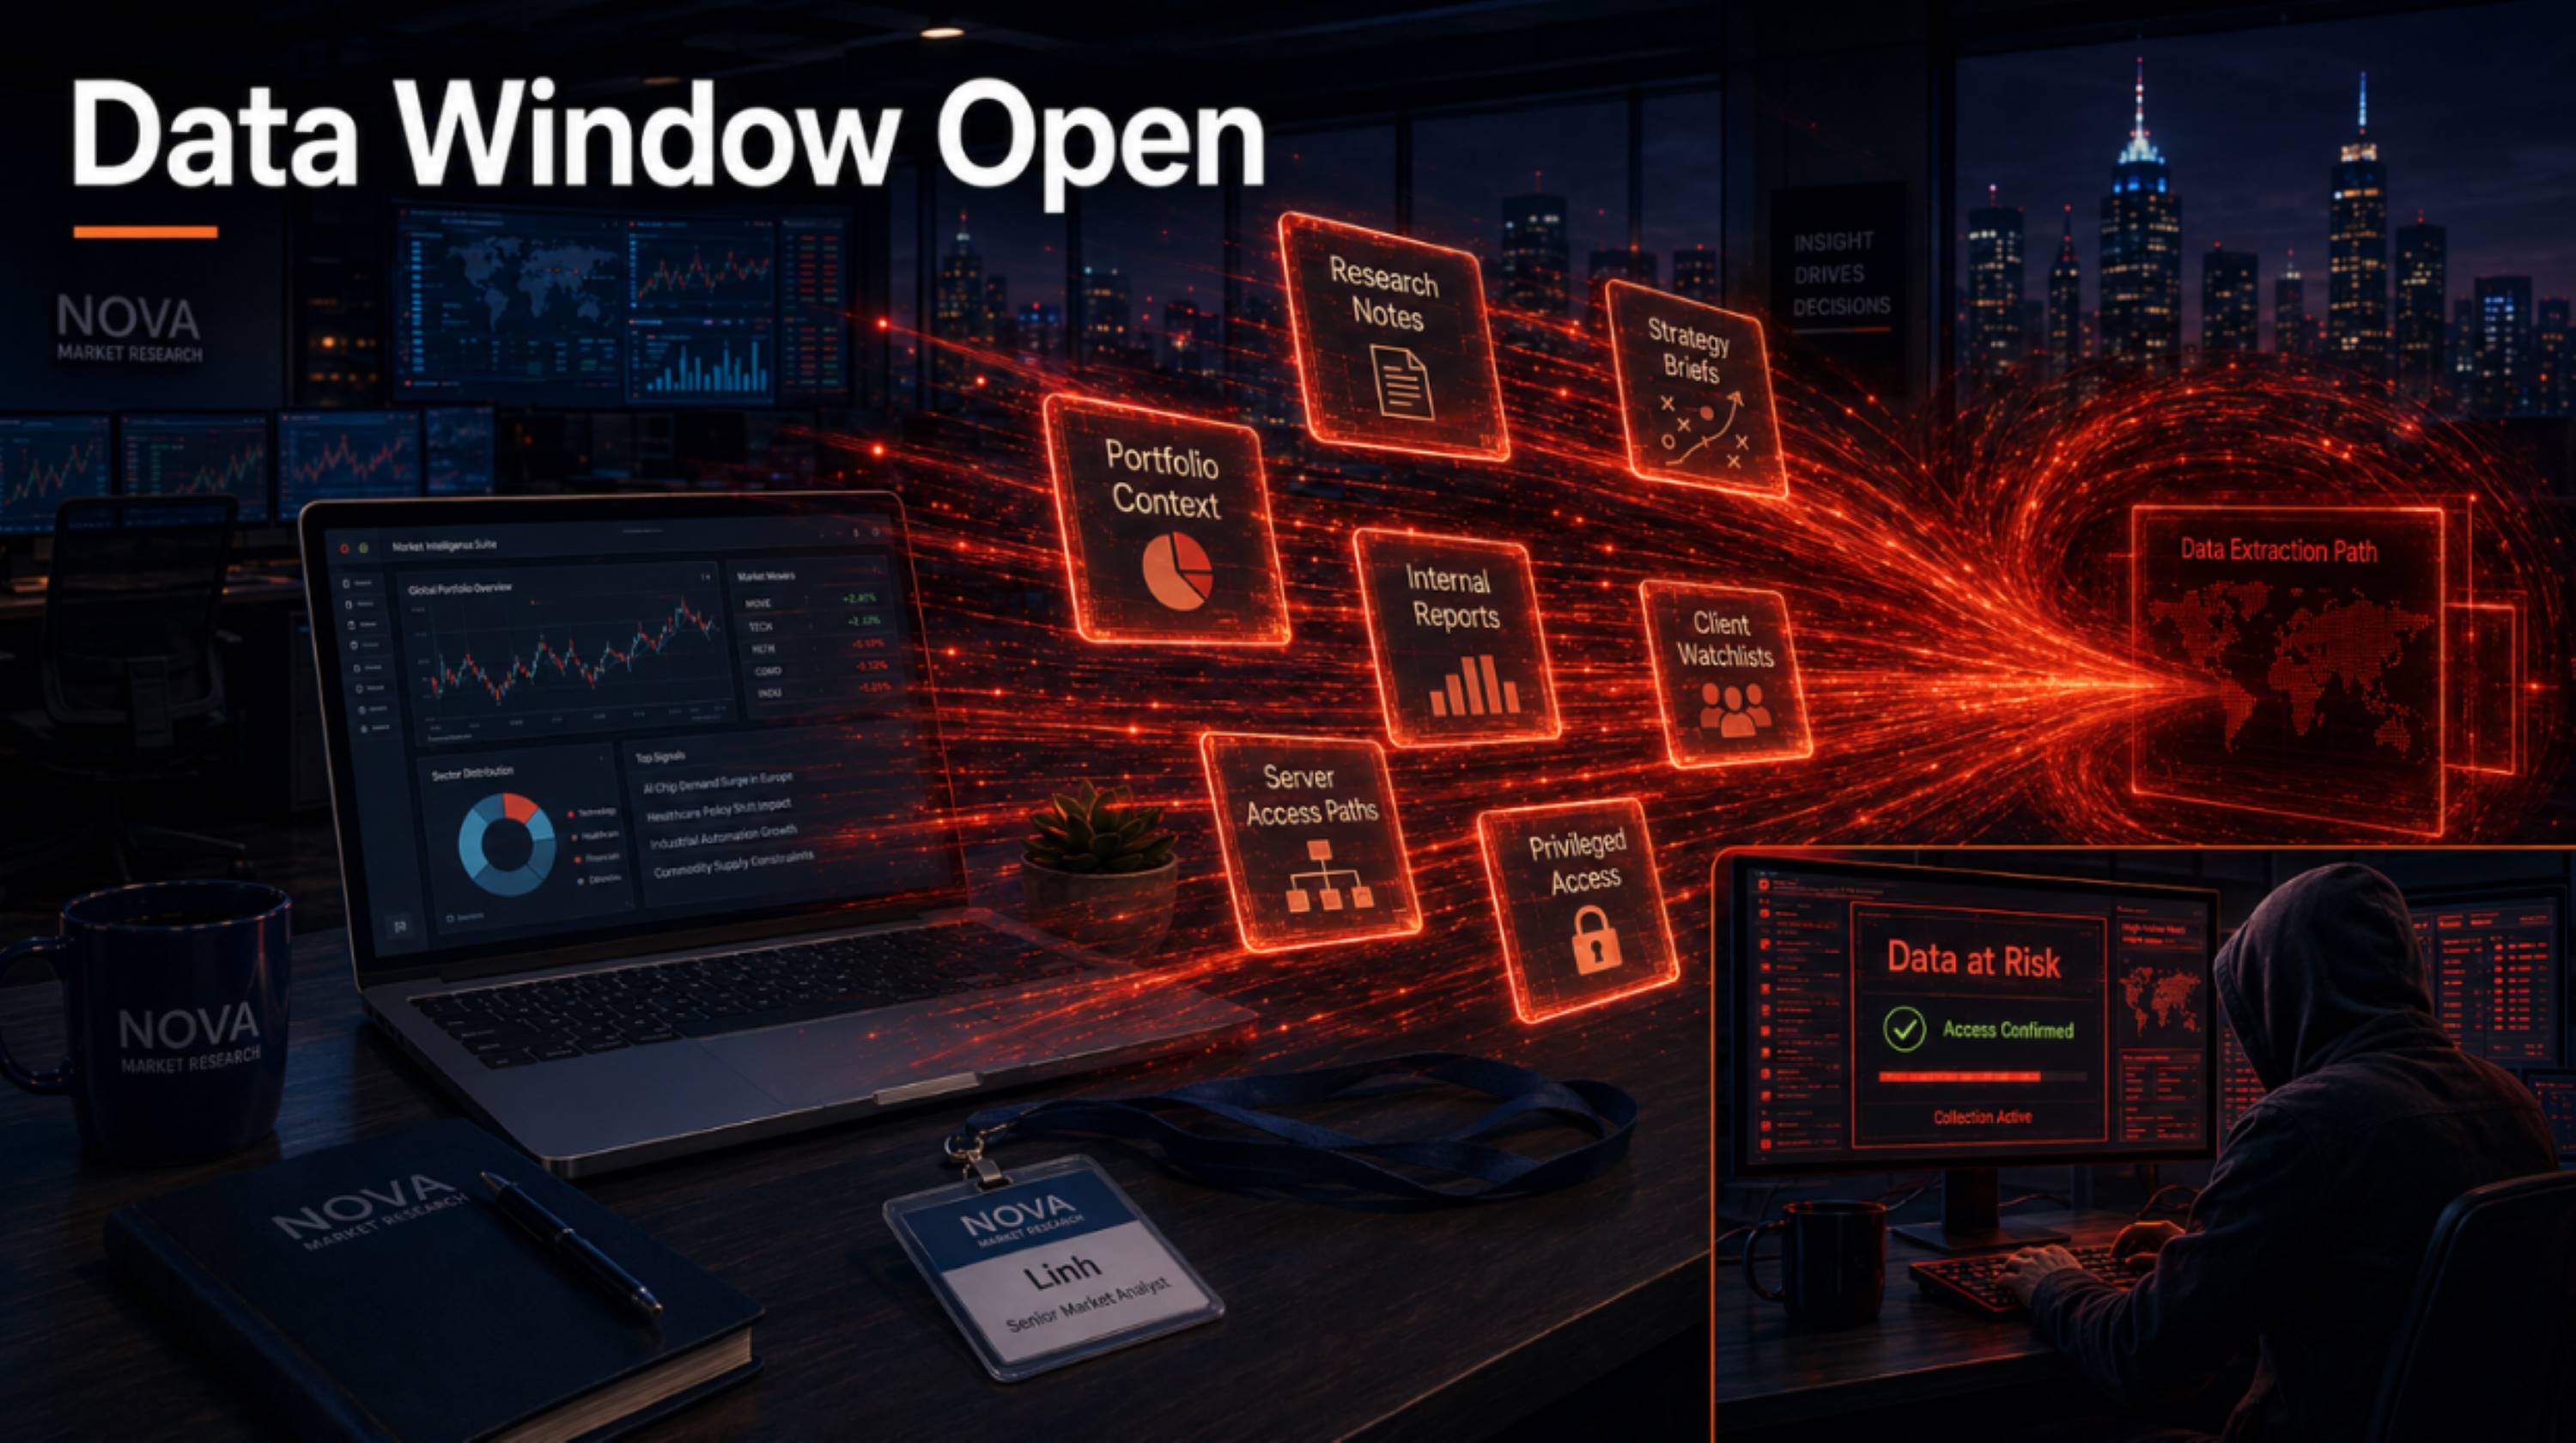
This scenario is designed to illustrate a defensive lesson: when attackers abuse trusted update paths, the most important signal may be a localized behavior change on a high-value endpoint, not a noisy outbreak across the whole organization.
Publication Note and Fictional Scenario Disclaimer: The comic above is a fictionalized scenario created to explain defensive concepts in clear business language. Nova Market Research, the characters, the market-data tool, the update prompt, and the operational details are illustrative. They do not refer to a real company, a real employee, a real product, or a specific confirmed breach.
The technical discussion that follows below is based on public cybersecurity reporting about activity associated with the publicly tracked OceanLotus/APT32 cluster. Attribution and activity interpretation in this article follow third-party public reporting and should not be read as an independent attribution claim by Sangfor.
Threat Overview
Public cybersecurity research has described activity associated with the OceanLotus/APT32 cluster involving the SPECTRALVIPER backdoor, including a software supply chain incident affecting a stock-investment-related update path used by investors in Vietnam and a separate intrusion involving a Vietnamese infrastructure and transportation construction organization. [1]
For defenders, the risk is the abuse of trusted, business-critical software channels to reach selected high-value systems while avoiding broad, noisy delivery patterns that traditional monitoring may detect more easily.
This article abstracts those public findings into practical defensive guidance for organizations that rely on local, industry-specific, vendor-controlled, or business-critical software update mechanisms.
Business Impact Summary
Trusted update abuse can be uniquely disruptive because it combines technical stealth with operational dependency:
- High-value business exposure: If a targeted endpoint belongs to an executive, senior analyst, financial planner, or privileged operations user, sensitive business context may become accessible to an attacker depending on local privileges and connected systems.
- Operational containment pressure: When the suspected delivery path is a tool the business depends on, security leaders may face a difficult containment decision: leave it running and risk continued exposure, or restrict it and disrupt daily operations.
- Delayed detection risk: Selective delivery can reduce obvious outbreak signals. A single unusual post-update event on a strategic workstation may matter more than a broad spike in alerts.
Technical Highlights
1. The Vector: Trusted, Business-Critical Software Updates
Public reporting describes a supply chain pathway involving a stock-investment-related software update mechanism. Rather than relying on mass phishing or noisy commodity malware delivery, the reported activity used a trusted software distribution path to place follow-on malware on selected systems. [1]
For enterprise defenders, the lesson applies beyond any one software product or geography. Any application that updates automatically, receives vendor-controlled packages, or operates with elevated trust can become a high-impact pathway if integrity validation, update transport security, and post-update behavior monitoring are weak.
2. The Payload: SPECTRALVIPER and Follow-On Access Risk
Public research has associated SPECTRALVIPER with OceanLotus/APT32-related activity. Public technical research has described SPECTRALVIPER as a heavily obfuscated Windows backdoor with capabilities including process loading or injection, file upload and download, file or directory manipulation, and token impersonation. [3]
In a defender-oriented risk model, an affected host may expose:
- System and user context, including host configuration and local operating conditions.
- Business application context, including files and access paths available to the logged-in user.
- Potential paths to additional systems, where credentials, shares, application sessions, or server access are present.
- Outbound command-and-control traffic that may appear similar to ordinary web or application traffic unless correlated across telemetry sources.
Defender-Oriented ATT&CK Mapping Based on Public Reporting
The mapping below is intended for defensive hunting and validation. It should not be read as an exhaustive or independently confirmed attack chain for every environment. Techniques should be applied where confirmed, where applicable, or where local telemetry supports the behavior being investigated. MITRE ATT&CK tracks APT32 as G0050 and lists OceanLotus among associated group names. [2]
| Attack Stage | Defender Question | Candidate ATT&CK Mapping | Signals to Validate |
| Delivery | Did a trusted software update path deliver different content to a small subset of users? | T1195.002 - Supply Chain Compromise; T1204 - User Execution, where user action is involved | Divergent update behavior; unusual package hashes; one or a few high-value endpoints receiving different files; unexpected updater network destinations. |
| Evasion | Did the new file appear legitimate because it used a familiar name, location, signature context, or trusted process relationship? | T1036 - Masquerading; T1553.002 - Code Signing abuse, where applicable | Signed, renamed, or familiar-looking binaries in application folders; file metadata mismatches; newly added modules beside trusted applications. |
| Execution and Loading | Did the trusted application load a new component or spawn unexpected child activity after the update? | T1574.002 - DLL Side-Loading, where observed; T1055 - Process Injection, where observed | Unexpected module load paths; new DLLs in application directories; abnormal child processes; memory injection signals tied to the business application. |
| Profiling and Discovery | Did the endpoint perform discovery activity immediately after a routine update? | T1082 - System Information Discovery; related discovery techniques where confirmed | Post-update system discovery; user/context enumeration; network or share discovery; staging requests for follow-on components. |
| Command and Control | Did the trusted application or a related process begin communicating with unusual external infrastructure? | T1071.001 - Web Protocols; T1573 - Encrypted Channel, where confirmed | Encrypted outbound beacons; rare domains; low-volume recurring traffic; proxy/DNS patterns that do not match the application baseline. |
| Data Access and Exposure | Did the affected host access sensitive files, credentials, or business systems outside its normal baseline? | T1005 - Data from Local System; T1041 - Exfiltration Over C2, where confirmed | Anomalous file reads; unusual archive creation; sensitive folder access; credential use from the affected endpoint; unexplained server access paths. |
Anomalous file reads; unusual archive creation; sensitive folder access; credential use from the affected endpoint; unexplained server access paths.
Educational Takeaway: Reassessing Software Supply Chain Trust
Public reporting reinforces a practical defensive lesson: a trusted source does not always guarantee a trusted outcome. Software origin, file reputation, and vendor familiarity are important, but they are not enough on their own. Security teams should replace passive trust assumptions with behavior-based verification:
- Trusted channels still need validation: Update transport security, code signing, manifest verification, package hashes, and release provenance should be reviewed for business-critical software.
- Business urgency can be exploited: Attackers may target tools that users and administrators are reluctant to block because they support trading, accounting, logistics, reporting, or operational workflows.
- Selective outliers matter: Traditional detection often focuses on broad anomalies. Supply chain abuse may appear as one high-value endpoint behaving differently after a routine update.
Self-Evaluation: Questions for Regional Financial and Enterprise Security Teams
- Which market data feeds, trading terminals, ERP clients, accounting tools, logistics platforms, or local business applications update automatically or through vendor-controlled channels?
- Do these update paths enforce TLS, integrity validation, code signing, and strict manifest verification wherever possible?
- Can detection tooling identify a case where only one high-value host receives a unique file or shows a localized post-update anomaly?
- Are endpoint controls hunting for suspicious module loads, unexpected application-folder changes, brief visual anomalies, post-update child processes, and persistence attempts?
- Can endpoint anomalies be correlated with DNS, proxy, firewall, identity, SaaS, and server logs within a single investigation timeline?
- Do high-value users such as executives, research analysts, financial planners, and privileged operations staff have stricter behavioral baselines than ordinary workstations?
- Is historical telemetry retained long enough to reconstruct what a trusted application did hours or days after a routine patch?
- Does the incident response plan include trusted-update abuse, vendor coordination, targeted threat hunting, containment decisions, and stakeholder communication?
Recommended Actions
- Audit and reclassify update paths: Treat trusted software update mechanisms as high-trust, high-impact assets. Include industry-specific software, vendor portals, local business applications, and auto-updaters in risk reviews.
- Enforce behavioral post-update verification: Do not rely only on the origin of a patch. Baseline post-update behavior and monitor for newly dropped binaries, uncharacteristic DLL loads, rapid child processes, and immediate outbound connections.
- Prioritize high-value outliers: A single executive or analyst machine behaving strangely after an update should be triaged with urgency, even if there is no broad outage or malware outbreak.
- Centralize and correlate telemetry: Link endpoint, DNS, proxy, firewall, identity, SaaS, and server access records so low-volume command-and-control or data access anomalies can be reconstructed.
- Prepare a targeted response playbook: Define how to isolate a suspected host, preserve evidence, coordinate with the vendor, review software integrity, and determine what sensitive context may have been exposed.
How Sangfor Helps
| Problem | Sangfor Solution |
| Limited visibility into application actions after updates | Endpoint detection, telemetry review, and targeted threat hunting focused on post-update application behavior. |
| Difficulty distinguishing routine maintenance from selective delivery | Managed detection and response workflows that correlate endpoint, network, and identity anomalies across high-value asset groups. |
| Slow validation across siloed logging tools | Cross-domain analysis that unifies endpoint, DNS, proxy, firewall, SaaS, and server logs into a coherent investigation timeline. |
| Weak controls over privileged or vendor-managed software assets | Access hardening, device health checks, least-privilege enforcement, and periodic reviews of vendor deployment loops. |
| Uncertainty about what sensitive context may have been exposed | Incident response support, compromise assessment, and forensic review of data-access anomalies and credential use. |
Call to Action
If your enterprise relies on local, industry-specific, or vendor-controlled software channels for daily operations, now is a good time to review post-update visibility. Moving from passive trust to active behavioral verification is one practical way to reduce the gap between assumed software integrity and actual operational assurance.
Legal, Attribution, and Use Disclaimer
This briefing is based on publicly available cybersecurity research and is provided solely for defensive awareness, threat hunting guidance, and educational reference. References to OceanLotus/APT32, SPECTRALVIPER, and related tactics reflect third-party public reporting and do not represent an independent attribution determination by Sangfor.
The narrative involving Nova Market Research, its personnel, and the generic market-data tool is fictional. It is intended to translate technical supply chain risk into clear defensive concepts. It does not describe any real security incident, company breach, software vendor compromise, government agency activity, or individual corporate compromise.
This document does not reproduce exploit code, live malicious infrastructure, or victim data. Descriptions of security capabilities are intended to explain risk-reduction support and should not be interpreted as a guarantee of complete prevention or absolute protection.
References and Public Source Notes
- [1] ESET Research, "OceanLotus: From external espionage to domestic targeting," WeLiveSecurity, June 11, 2026.
https://www.welivesecurity.com/en/eset-research/oceanlotus-external-espionage-domestic-targeting - [2] MITRE ATT&CK, "APT32, SeaLotus, OceanLotus, APT-C-00, Canvas Cyclone, BISMUTH, Group G0050."
https://attack.mitre.org/groups/G0050 - [3] Elastic Security Labs, "Elastic charms SPECTRALVIPER," June 9, 2023. https://www.elastic.co/security-labs/elastic-charms-spectralviper